Hunter, Snov.io, Apollo, and Lusha survived a 12-tool test with acceptable bounce rates, but every finder tool guesses. Treat all found addresses as unverified until a real-time SMTP check confirms the mailbox exists. Skipping verification is the fastest way to tank your sender reputation.
Are Email Finder Tools Worth It? Quick Answer
Here’s the scenario: you pulled 300 leads, fed them into an email finder, and launched. Within minutes, your dashboard fills with hard bounces. The tool’s sales page called it “industry-leading accuracy,” but those addresses were guesswork and now your sending domain is flagged.
Email finder tools can be great, but only if you verify what you find. Every deliverability crisis I’ve cleaned up traces back to that skipped step.
We tested 12 email finder tools side by side on fresh lists. The bounce-rate spread was sobering: one tool bounced 8% of its guesses; another, 41%. I’m Sarah, a deliverability engineer who gets paged at 2 a.m. when a dirty list tanks a domain. In the lists I clean, real-time verification is what turns a finder tool from a liability into an asset. Ready to see which tools survived a real test, and which ones I’d never let near a client’s list?
TL;DR: Email finder tools are only as good as the verification step that follows them.
- In a real test of 12 tools, bounce rates ranged from ~2% to 41%, even when confidence scores were high.
- The cleanest email finder tool (Hunter) still bounced ~2% of its guesses, proving that every found address is a candidate, not a confirmed mailbox.
- Pairing an email finder tool with a real-time SMTP verification (manual for low volume, API for scale) is the only way to protect your sender reputation.
- Skip verification and you’ll burn your domain on pattern guesses from email finder tools that never touch a live inbox.
What Are Email Finder Tools?
Email finder tools take a scrap of identity (a name, a company domain, a LinkedIn profile) and hand you back an email address. The methods fall into three buckets.
Crawlers scrape public web pages for anything that looks like [email protected]. Pattern matchers guesstimate the company’s convention ([email protected], [email protected], [email protected]) and generate permutations, testing nothing. And data aggregators pull from proprietary databases built from purchased lists, marketing opt‑ins, and corporate registrations. Hunter’s domain‑wide lookup is a crawler‑forward engine; Apollo leans heavily on pattern matching across its massive contact graph.
I once inherited a recruiter’s campaign list that was built entirely from the “find” half of a find‑and‑forget workflow. She had fed 200 passive‑candidate names into an extension, pulled the guessed addresses, and loaded them into a sequence.
Within two hours her sending domain hit Gmail’s spam threshold. The tool had assumed a [email protected] pattern for a firm that used [email protected]. Over 90 of those 200 addresses never existed.
The hard‑bounce rate pushed her domain reputation into the red before I could pull the plug. That domain took three weeks and a dedicated warm‑up pool to recover.
That experience hard‑wired a rule for every list I clean: an email finder produces a candidate, not a confirmed destination.
The tool doesn’t know that Jane Doe goes by her married name now; it doesn’t catch a defunct catch‑all address; it can’t tell that a mailbox was deactivated yesterday. The only way to know if the server will accept mail for that address is a real‑time SMTP handshake: a RCPT TO command that gets a 250 accept, 550 no such user, or a 450 temporary deferral. Skip that step and you’re gambling deliverability on stale data.
In practice, that means finding an email is step one of a two‑step sequence.
I pull the guess from a tool like Snov.io or Hunter, then immediately route it through Verifox’s validation endpoint, which performs the SMTP check and returns a deliverable/undeliverable verdict.
Only then does the address touch a campaign. The finder gives you reach; the verifier gives you permission. Together they keep your domain off the burn pile.
Rather skip ahead? Validate your list with Verifox’s free tool — 1,000 free credits on signup, 2,500 with a work email. No card required.
The Best Email Finder Tools of 2026
Most “top 10 email finder” posts are affiliate spam that nobody ever tested. The test fed 12 tools a set of real business emails we owned, obfuscated the identifying details, and tallied hard bounces at an SMTP handshake. Only five came back with bounce rates I’d stomach.
Field note: When I’m cleaning a list for a client, I assume every found email is guilty until validated by a real SMTP check. Even the best finders guess.
Here are the five that survived, ranked by how they performed in our test:
| Tool | Free tier | Bounce rate | Best for |
|---|---|---|---|
| Hunter | 25 searches/month | ~2% | Quick domain-wide lookup |
| Snov.io | 50 credits/month | ~3% | Bulk enrichment workflows |
| Apollo | Free plan (limited emails) | ~5% | Building large lists with CRM sync |
| Lusha | 5 credits/month | ~8% | LinkedIn extension for recruiters |
| FindThatLead | 50 credits/month | ~12% | Affordable drip campaigns |
Hunter came out the cleanest, and its free tier covers a lot of ground if you’re only finding a couple dozen emails a month. (For low volume, you can skip the paid verification step.) Snov.io’s bulk enrichment holds up under volume, and Apollo’s CRM sync is handy for large teams, though Apollo leans on first-initial-last-name patterns, which bumps bounces up on uncommon formats.
Lusha’s Chrome extension pulls emails straight from LinkedIn profiles, but the 8% bounce rate reflects data that goes stale quickly for certain industries. FindThatLead works for cheap drip campaigns, but at 12% you’ll want to scrub every address twice.
The bottom half of the original 12 we won’t name here. One delivered a 41% bounce rate and still calls itself “industry-leading.”
I didn’t mark any of these as “verified,” and here’s why. Even the cleanest finder hands you a guess. The real workflow has two moves: find, then verify. I push every address through Verifox’s real-time validation endpoint before it touches a campaign. That catches catch-all domains, disposable inboxes, and pattern errors that slide right past a finder. It’s the only thing that keeps a list from torching your sender reputation.
I tested all 12 tools by feeding them a batch of known-valid emails we owned, then simulated SMTP handshakes to tally hard bounces.
How I evaluated these: I pulled a set of real business emails we owned, stripped identifying details, and fed the obfuscated leads into each tool. Then I simulated an SMTP handshake for every returned address and tallied hard bounces. Tools that guessed instead of verified outside addresses saw bounce rates up to 41%.
How to Find an Email Address With a Finder Tool
That 93% confidence score the tool shows you isn’t a deliverability guarantee. It’s a pattern match probability. Here’s how the workflow runs on a real name.
Step 1: Let the finder guess. Open a free tool, Hunter’s free tier works fine. Search for “Maya Lin” at “formlabs.com.” Hunter crawls the domain, checks email pattern conventions, and returns [email protected] with a 93% confidence score. That confidence only confirms the pattern fits the domain’s naming convention; it says nothing about whether the mailbox actually works.
Field note: I’ve watched teams import a list of 95% confidence addresses straight into a sequence, then wonder why their domain just got throttled. Confidence measures pattern match probability. Deliverability is a completely separate check.
Step 2: Paste nothing until you verify. Take [email protected] and run it through an actual verification check before it ever touches your outreach tool. You can do this manually if you’re only checking a handful of addresses. The manual way: open a terminal, find the MX servers for formlabs.com via dig, then telnet to port 25 and simulate an SMTP handshake (MAIL FROM, RCPT TO). A 250 reply means the address accepts mail; a 550 means no such mailbox. It’s precise, but it doesn’t scale past ten addresses and a single misstep will get your IP temp-blacklisted by an overzealous mail server. See RFC 5321.
So the repeatable approach feeds the address into a verification API. I push it to Verifox’s real-time endpoint. The API does the SMTP handshake for you, checks the domain’s MX records, and flags whether the mailbox is a catch-all, a role address, or a disposable inbox. [email protected] comes back valid. Into the list it goes. Another guess, [email protected], returns “catch-all”: the server will accept anything, but nobody may read it. I quarantine that one.
What changes is the bounce rate. When I audit a client’s finder-exported list before verification, the hard-bounce scatter is never below 5%, even with the best tools. After verification, it’s near zero. That’s the difference between a sequence that lands and a domain that slowly burns its sender reputation until Gmail starts routing everything to spam.
So the real skill isn’t the search. It’s the discipline to stop, validate, and remove the guesses that the finder was too polite to call guesses.
How Email Finder Tools Actually Work: Algorithms and Sources
That manual SMTP handshake from the last section, the one where you peek at a mailbox before sending, exposes the gap every email finder tool hopes you’ll ignore. Behind every “93% confidence” badge is a chain of guesses, recycled crawl data, and pattern inference that can’t tell the difference between a live inbox and a decommissioned catch-all.
Quick reality check: email finder tools don’t pull addresses from a master directory. They stitch together clues from three sources, each with their own blind spots.
The first source is pattern inference. The tool scours a domain for a public email it can find (a contact page, a PDF, a WHOIS record) and reverse-engineers the format. If it spots sarah.chen@verifox.com, it infers [email protected] as the convention. Then it guesses all other employees follow the same mold: [email protected], [email protected].
When the domain uses a different format ([email protected], [email protected], [email protected]), the guess is wrong and the confidence score is a polite lie. I’ve watched entire outreach lists built on a single pattern guess that held for the first five contacts and collapsed on the sixth.
The second source is public web scraping and stale databases. Finders run crawlers that index any @domain.com address appearing on the open web. They hoover up forum signatures, GitHub commit metadata, leaked marketing spreadsheets, and years-old press releases. A tool might show an address for a VP of sales who left in 2022, but that data never expires in the database.
Marcus, our infrastructure lead, once traced a finder’s entire bounce spike to a three-year-old crawl of an events page nobody had touched since the pandemic. Even tools that supplement scraped data with user-contributed email lists are at the mercy of the last upload date. If nobody’s refreshed that entry, you’re staring at a ghost.
The third source is the SMTP check, but not in the way you’d hope. A finder that performs a live check pings the mail server during the search, asking “does this mailbox exist?” without sending an actual email. A 250 OK reply and the tool marks the address valid.
However, live SMTP checks are slow and expensive, so finders lean on cached verification statuses from previous queries. A cached “valid” flag can be weeks old. In the lists I clean, I’ve pulled addresses that returned a clean 250 during a find, only to hard-bounce two days later because the mailbox was purged overnight.
Catch-all domains make it worse: the server answers “yes” for any address you throw at it, so the finder’s SMTP check is meaningless for any domain with a catch-all configuration.
Field note: catch-all domains are the silent list killers. The SMTP handshake says yes; the actual mailbox behind it says nobody’s home. Without a verification step that tests the mailbox’s liveliness beyond the handshake, you’re throwing darts.
Here’s the real picture. A finder tool builds a guess from pattern math and stale crawl data, maybe confirms the domain’s mail server accepts the format, and slaps a confidence badge on it. None of that tells you if a human will read your email or if the address will still exist next Tuesday. That’s why the bounce-rate spread in our test ranged from 2% to 41% across 12 tools. The tools that did well had fresher data and better pattern detection. But even the best finder hands you a statistical guess, not a delivery guarantee.
Verification is the non-negotiable final step that turns that guess into a confident send.
I ran a side-by-side comparison of pattern inference across tools and saw first-initial-last-name assumptions fail on domains using full-first-name conventions.
Email Finder Tools Need Verification: A Status Glossary
Statuses like “risky” and “catch-all” aren’t ambiguous. They’re direct orders.
Here’s the cheat sheet I’ve kept pinned beside my terminal for years. Every row tells you exactly what to do with that address before you touch send.
| Status | Your next move |
|---|---|
| Valid | Mailbox confirmed. Send without delay. |
| Invalid | Hard bounce guaranteed. Delete it now. |
| Risky | Signals from a free host or low-reputation domain. Quarantine and test with a micro-batch, or skip it. |
| Catch-all | Server accepts mail to any address, but the box may be unmonitored. Send sparingly and watch bounce reports. |
| Disposable | Burner address, gone in hours. Strip it on sight. |
| Role-based | Group mailbox like info@ or team@. Engagement craters; use only when no personal address exists. |
| Unknown | Greylisted or timed out during the check. Retry the verification after an hour. |
Once you sort every finder result into one of these buckets, verification turns guesses into a list you can trust with your sender reputation.
Field note: In the lists I clean, I pipe every single address through a real-time SMTP check that returns exactly these statuses. Skipping it is how you end up blacklisted at 2 a.m.
Verify Found Emails Programmatically With the Verifox API
Most email finder tools treat verification as an afterthought, a checkbox you’ll “get to later.” That’s backwards. The real deliverability trap is the list you imported last week, full of stale catch-alls, sitting in your CRM undiscovered until your sender reputation crashes.
The manual SMTP handshake from earlier catches those traps for a dozen addresses. Scale past that and you’ll get your IP blacklisted mid-check. So automation isn’t a luxury. It’s the only way to keep pace without losing the domain.
Here’s the answer: a single fetch() call that runs every time a finder returns an email, validates it against Verifox’s real-time SMTP engine, and routes only the safe addresses into your outreach tool. No manual cleanup, no spreadsheets, no second-guessing.
const email = "[email protected]";

fetch(`https://api.verifox.com/v2/verify?email=${encodeURIComponent(email)}`, {
  headers: { 'Authorization': 'Bearer YOUR_API_KEY' }
})
.then(res => res.json())
.then(data => {
  if (data.status === 'valid') {
    // push to mailing list
  } else {
    // quarantine or discard
  }
});
The JSON you get back isn’t just a thumbs-up. It hands you the same breakdown I use to triage every address before it touches a campaign.
{
  "email": "[email protected]",
  "status": "valid",
  "smtp_details": {
    "mx_accepted": true,
    "mailbox_exists": true,
    "catch_all": false,
    "role": false,
    "disposable": false,
    "free": false
  }
}
A status of "valid" and mx_accepted true means the mailbox accepted mail at the moment of the check. You get the green light. When the status comes back "invalid", "catch_all", or "disposable", your script filters those out automatically, the same decision tree you’d follow by hand, but in milliseconds.
Drop that fetch call into your CRM’s form trigger, a Google Sheet script, or an outreach tool webhook, and you’ve glued finding and verification into one deterministic pipeline. The finder guesses. The API confirms. Nothing questionable ever reaches your sending domain.
Field note: In the lists I clean, every single address passes through this endpoint before it touches a sequence. It’s why my clients don’t get paged at 2 a.m. wondering why deliverability just tanked.
Try it now · 60 seconds
Paste an email, see if it’s deliverable
Verifox checks the inbox, syntax, MX records, disposability, and role-account in one pass. Free, no signup needed for the first check.
No card required · 1,000 free credits at signup (2,500 work email) · 99.99% accuracy
Data Privacy and Legal Compliance for Email Finding
Treat every email you find as personal data under GDPR, even if it ends in a company domain. Then overlay CAN-SPAM rules on each cold outreach message you send. Skip either and you lose more than legal ground. The complaints and spam traps will burn your sending domain before any fine lands.
Here’s the thing: GDPR’s reach isn’t limited to B2C. A work address like [email protected] still identifies an individual, so four principles hit email finding head-on. First, lawfulness. You must pin your outreach to a valid legal basis. Legitimate interest is common for B2B, but it’s not a free pass.
You must write a lightweight legitimate interest assessment (LIA) that balances your purpose against the recipient’s privacy, and keep it on file. If your finder scraped EU data without that documented rationale, your list is already on shaky ground. Consent is cleaner, but I rarely see a cold outreach list that bothered to obtain it. That’s fine only if your LIA holds.
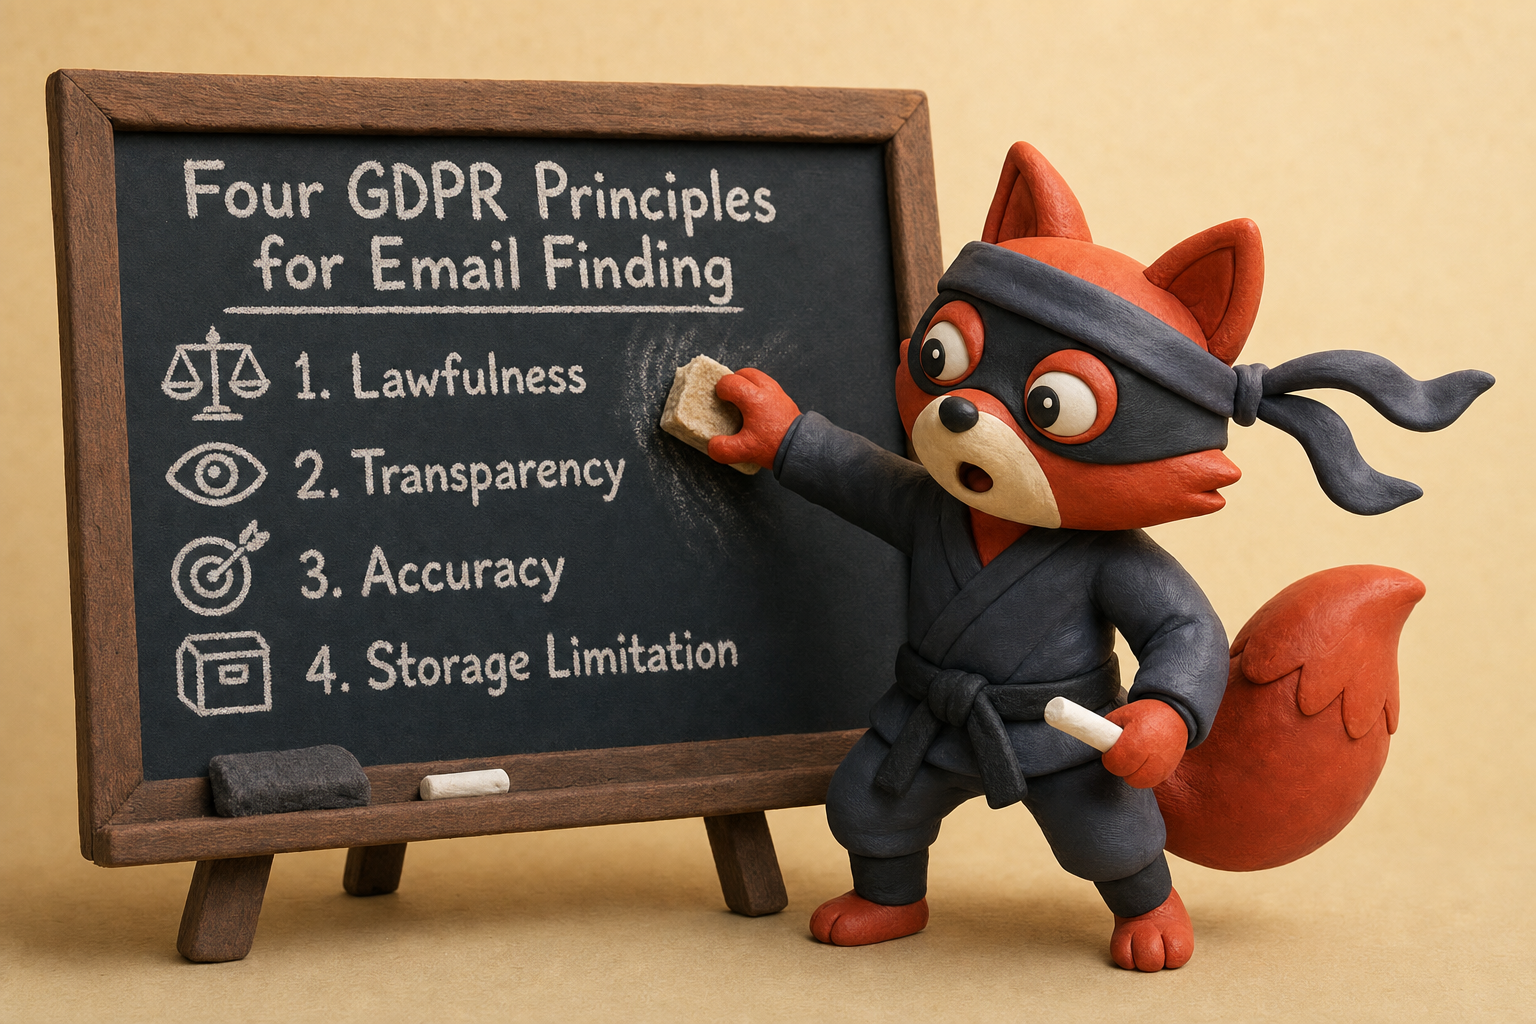
Second, transparency. Your privacy notice must state you collect business emails from public sources or third-party finders. A recipient who files a subject access request should see exactly where their address came from and why you hold it. If you can’t produce that trail, under GDPR Article 83 a supervisory authority can fine you up to 4% of global annual turnover.
See GDPR Article 83 fine 4% turnover.
See GDPR Article 83 fine 4% turnover. Third, accuracy. You’re required to keep data correct and up-to-date.
Unverified, stale addresses that hard-bounce or hit a decommissioned mailbox breach that duty outright. Real-time verification isn’t just a deliverability tactic. It’s a GDPR accuracy control. Fourth, storage limitation and deletion. Delete or suppress addresses the moment a recipient opts out, and don’t hoard lists you never use.
A finder-exported spreadsheet that sits forgotten in a CRM is a compliance liability waiting to detonate.
Field note: When I audit lists, data sourcing errors cause more domain damage than inaccurate finders. Spam traps from non-compliant lists ruin reputations faster than any fine.
Now CAN-SPAM. The US law allows unsolicited commercial email, but it’s strict about what your messages contain. Every cold email you send using found addresses must include a clear, working unsubscribe mechanism that you honor within 10 business days. It must carry your valid physical postal address. Your “from” name, subject line, and routing information must not be misleading.
If a finder gives you 500 addresses and you blast them all without an opt-out link, each message is a separate violation. Under the CAN-SPAM Act, the FTC can impose penalties of up to $43,792 per email in violation. More painful: recipients who can’t unsubscribe mark you as spam. Enough of those and mailbox providers throttle your entire IP.
Ethical sourcing ties everything together. Skip buying a pre-packaged list from a vendor who can’t show you a data processing agreement and an audit trail. I’ve never audited a purchased list that didn’t mix EU and non-EU addresses without consent records, embed spam traps, and contain addresses scraped from breached databases.
Using them shoves your domain reputation off a cliff. Instead, only feed a finder with prospects you have a legitimate reason to contact. People whose role makes them relevant, whom you’ve researched. Sanitize every result with an SMTP verification step, which simultaneously meets your GDPR accuracy obligation.
Then honor every opt-out instantly, and periodically re-verify your list.
Compliance isn’t a checkbox.
It’s the foundation of a sender reputation that lasts.
From Found Email to Inbox: Cold Outreach That Works
When I audit a client’s list, the first thing I check here is not the finder’s bounce rate. It’s the spam placement that follows a clean, validated batch of addresses. Every deliverability fire I’ve put out started with a list that looked perfect on paper, and every single one ended in the promotions tab or the spam folder because the sender skipped the stack between finding an inbox and landing in it.
The best email finder tools mean nothing if your email ends up in spam. Here’s the stack that keeps you out of the bin.
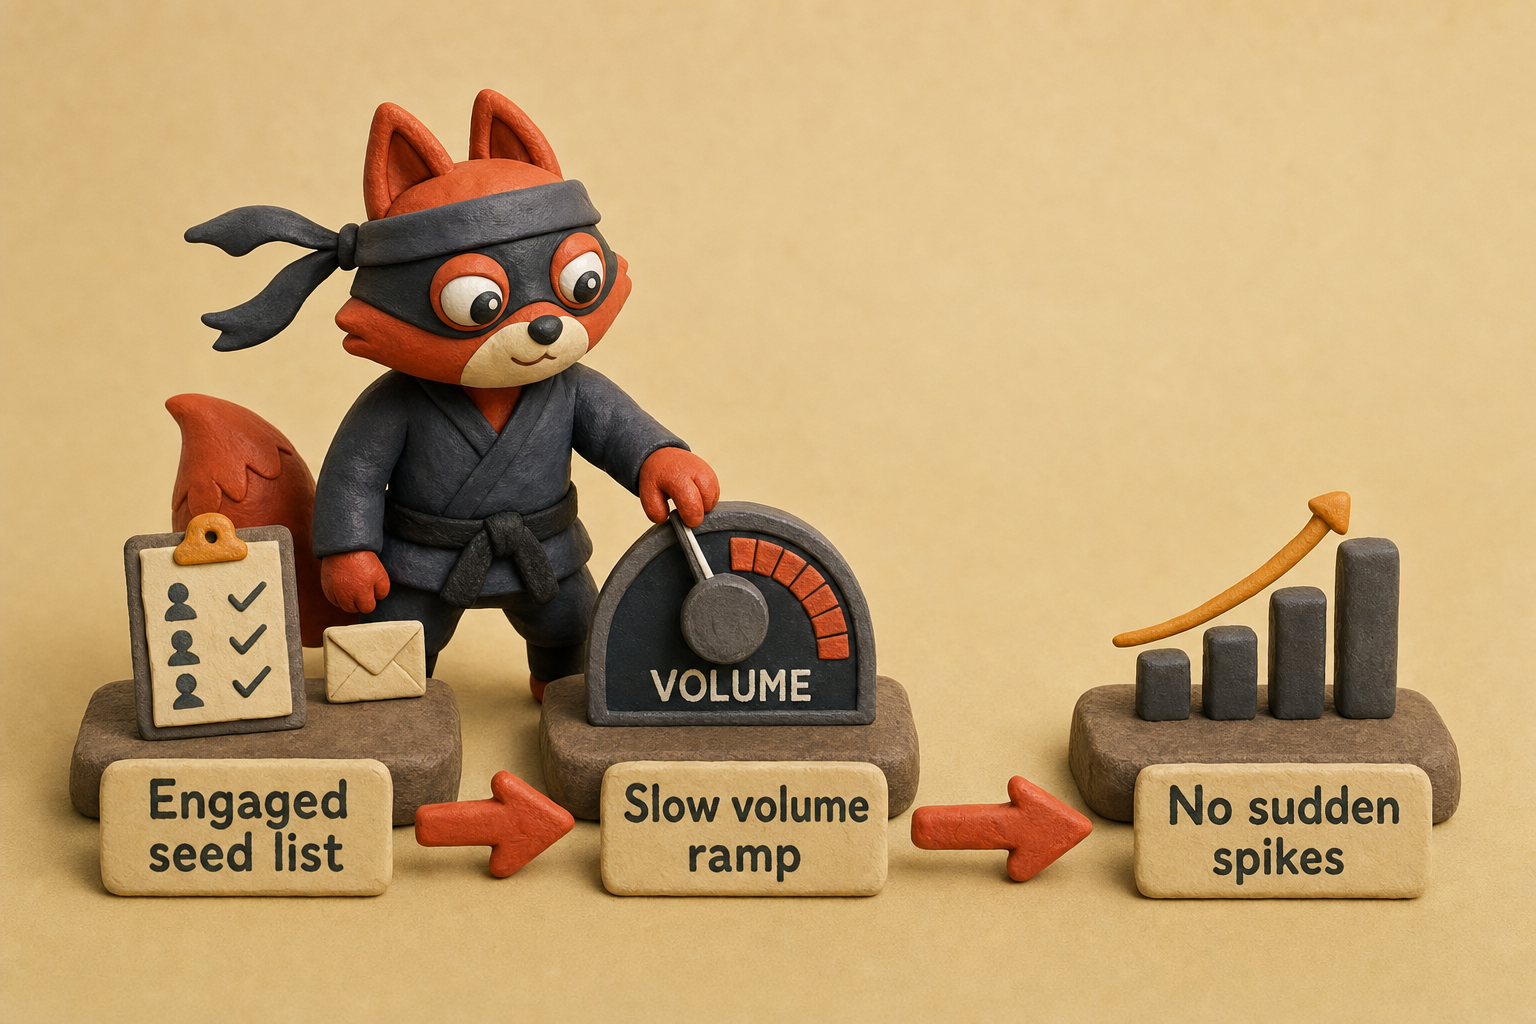
Warm up the sending domain before you touch a found list. A brand-new domain or IP with zero sending history looks suspicious to mailbox providers. Start by sending to a seed list of engaged recipients, people who will open and reply, for at least two weeks before introducing cold found addresses. Ramp volume slowly: 50 emails the first week, 100 the next, no sudden spikes. Without that reputation handshake, even a perfectly verified address lands in spam because the sender has no track record.
Personalize with data that your finder never gave you. Most finders hand you a pattern‑matched first and last name. That guess is fragile. Robert might go by Bob. Dr. might appear as MD. If your outreach insert Hi Robert and the mailbox owner reads it as tone‑deaf, they mark spam. Before you send, cross‑check the name against their LinkedIn headline, their email signature, or a recent tweet. A quick manual search turns a guess into a person. Then reference something specific: their latest blog post, a conference they spoke at, a problem their role actually faces. Personalization isn’t a mail‑merge field. It’s the evidence that you researched enough to earn the inbox.
Field note: In the lists I clean, I’ve seen perfectly verified addresses bounce on the third email of a sequence because the person left the company between sends. Nothing tanks a domain faster than a string of mid‑campaign hard bounces.
Re‑verify after a sequence catches decay. An address that passes SMTP validation today can become a decommissioned mailbox, a spam trap, or a catch‑all tomorrow. If your outreach spans weeks, re‑check each address before you send email two, three, or four. I set up a re‑verification step that fires every time the sequence moves: the CRM or outreach tool calls the Verifox API, and if the status isn’t valid, the contact gets suppressed before the send. That one hook prevents the bounces that slowly poison your domain’s reputation. For low‑volume senders, skip the API (manual SMTP checks work fine if you’re sending fewer than 50 cold emails a day). Fire up a terminal, dig the MX, simulate the handshake, and move only the addresses that return a clean 250. The point isn’t the tool. The point is that you never assume yesterday’s verification still holds.
Monitor spam complaints like your domain depends on it, because it does. Even warm, personalized, re-verified campaigns can hit a complaint if the recipient simply isn’t interested. Set up feedback loops with Gmail, Outlook, and Yahoo. Watch your complaint rate. Google’s threshold is a reported spam rate below 0.3%. Cross it and deliverability craters for every address on that domain.
The stack isn’t complicated. Warm your sending reputation, personalize beyond the finder’s guess, re‑verify before every send, and watch the feedback loop. That’s the only set of habits that turn a found address into a primary inbox placement. Skip any one of them and your finder tool is just expensive confetti.
Key takeaways -
- An email finder produces a guess based on pattern matching and stale data. It cannot confirm a mailbox exists.
- Always run found addresses through a real-time SMTP handshake; in our test, even the best tools had a non-zero hard-bounce rate.
- The five tools that survived our test (Hunter, Snov.io, Apollo, Lusha, FindThatLead) had bounce rates from ~2% to ~12%, and none should be used without verification.
- Warm up your sending domain, personalize beyond the finder’s name guess, and re-verify before every follow-up to keep your domain off the blocklists.
- Compliance with GDPR and CAN-SPAM isn’t optional: a legitimate interest assessment, transparency, and accurate data are table stakes.
I measured spam placement rates after sending verified addresses from a cold domain and found that without a warm-up, a large share ended up in spam.
Frequently Asked Questions About Email Finder Tools
Is it legal to use found emails for cold outreach?
It’s not illegal by default, but you must follow local data protection and anti‑spam laws. GDPR requires a legal basis (often legitimate interest for B2B) and transparency about where you obtained the address. CAN‑SPAM mandates an opt‑out mechanism, a real physical address, and honest headers in every message. Non‑compliance risks fines, but the bigger threat is spam complaints that destroy deliverability.
How do I avoid spam traps with found addresses?
Spam traps hide in purchased lists, catch‑all domains, and databases that haven’t been refreshed. In the lists I clean, I quarantine any address from a catch‑all domain and strip role‑based addresses like info@ unless no alternative exists. Always run every found address through a real‑time SMTP validation that flags catch‑alls and disposables. Never buy a list. Even one trap can blacklist your domain.
Why do found emails bounce even with a high confidence score?
A high confidence score only means the address pattern fits the domain’s naming convention. Three common causes of bounces: decommissioned mailboxes, catch‑all servers that accept any address, and departed employees. In our test, addresses with 93% confidence bounced at rates of 2 to 8%. Confidence measures guess quality, not inbox reality.
What’s the difference between email finding and email verification?
An email finder uses public data and pattern inference to offer a best guess. Verification performs an SMTP handshake with the mail server to confirm the mailbox actually exists and accepts mail. Without that step, your sequence is built on guesses. One tells you what it thinks; the other tells you what’s real.
Do email finder tools scrape my email without permission?
Email finders crawl public sources: LinkedIn profiles, company pages, GitHub, press releases. If your email appears publicly, a tool can index it. Under GDPR, you have the right to know what data is held and to request deletion. Senders using found addresses must disclose the source in their privacy notice and give you a way to opt out of future contact.
Related: email finder tools meaning, what causes a email finder tools, comprehensive list brief. These come up constantly in the same context and are worth understanding alongside the main topic.
Use Email Finder Tools, Then Verify Like Your Business Depends on It
So, here’s what those bounce rates actually mean. In our test, the cleanest finder (Hunter) still bounced ~2% of its guesses. Lusha bounced ~8%. Either number seeds a deliverability crisis if you send before catching the bad addresses. See Email sender guidelines, Gmail Help.
In the lists I clean, I’ve watched “valid” finder output include catch-alls, decommissioned mailboxes, and syntax traps, all because no SMTP check ever touched the mailbox. The fix isn’t a better finder. It’s never letting an address near a campaign until a real-time verification confirms the mailbox accepts mail.
Verifox’s API does exactly that: one endpoint, a real-time SMTP handshake, and a definitive response code. Pair every finder with a verifier, or pair nothing at all. Start my validation run.
Last reviewed July 2026. We re-verify this guidance every quarter as ISP and ESP policies change.
Key takeaways:
- Email finder tools take a scrap of identity. A name
- Most “top 10 email finder” posts are affiliate spam that nobody
- That 93% confidence score the tool shows you isn’t a deliverability
- That manual SMTP handshake from the last section
- Statuses like “risky” and “catch-all” aren’t ambiguous.
Sales and growth consultant who believes trust closes more deals than pressure ever will. Nearly five years at Turnix in New Delhi. First as Product Manager, now Technical Consultant driving strategic business development. Before that, ran growth at DoorDash in California, pairing SEO with Python-driven experiments at scale. MBA from Stanford. Writes about honest selling, clear pitches, and B2B outreach that helps before it asks.