A soft bounce email is a temporary 4xx delivery failure (a full mailbox, greylisting, or a server timeout) not proof the address is dead. Read the enhanced status code, retry on your ESP's schedule, fix signup data collection before touching send frequency, and suppress any address after five consecutive soft bounces.
Quick Answer: What Is a Soft Bounce Email?
You send a campaign and the report flags a soft bounce email: the server answered, but didn't deliver. That's a temporary delivery failure; it says nothing about address quality. SMTP reply codes in the 4xx range, defined in RFC 5321, mean "not now."
A mailbox is full, a server is greylisting you, or the connection times out. See RFC 5321: Simple Mail Transfer Protocol. A 5xx reply means "no, permanently," which is a hard bounce.
Temporary does not mean harmless.
Most soft bounces clear after a few retries on your email service provider's schedule. Repeated soft bounces on the same address teach inbox providers that you don't know your list. That's the quiet cost that chips away at sender reputation. In my experience, a 4xx deferral maps to a specific temporary condition-a full mailbox, a content filter, a throttled connection-and the exact code tells you which lever to pull. Ready to fix the root cause before soft turns hard?
Soft Bounce Email Meaning: Transient Failure, Not Rejection
RFC 5321 calls a 4xx reply "transient negative completion": the server answered, but the mailbox refused the message right now. See Simple Mail Transfer Protocol. That refusal covers two situations.
Infrastructure failure: a mailbox over quota returns 452, a server under load returns 450, and greylisting returns 451 with a retry hint. A connection timeout produces no 4xx code at all. Policy throttling: the server defers you on purpose for volume, IP reputation, or rate limits.
None of these say the address doesn't exist.
Conventional advice lumps all of that under "temporary." A full mailbox clears on retry. Rate limiting won't.
Check the enhanced status code from RFC 3463 after the 450 or 451. 4.2.2 means the mailbox is full, so wait. 4.7.1 means adjust your cadence or IP warmup.
Rather skip ahead? Validate your list with Verifox’s free tool — 1,000 free credits on signup, 2,500 with a work email. No card required.
What Causes a Soft Bounce Email?
A soft bounce email comes from two groups: transient infrastructure failures and deliberate policy decisions. The bounce report collapses both into one label, and full mailboxes appear first, so they dominate the conversation. That focus hides the content and authentication failures underneath. Reading the difference determines whether you wait, adjust the content, or repair DNS.
Capacity failures
A mailbox over quota is the classic infrastructure failure. The address exists, but the recipient's storage is maxed. The server returns 4.2.2, meaning mailbox full, and tells you to try later. It clears when the recipient deletes or archives mail. Shared inboxes and distribution lists fill up fastest because one heavy inbound message can push every member over the limit.
Message size limits land in this bucket, too. Each receiving domain sets its own cap. A PDF deck with embedded screenshots can sit just under your sending limit but over the recipient's. The retry sends the same oversized weight again, so the bounce won't clear on its own.
Server-side deferrals
A server timeout or temporary outage hides behind a 450, a dropped connection, or no reply at all. In a raw bounce log, a 450 appears as an SMTP error line with the receiving server's temporary failure note, a dropped connection appears as a connection reset or no banner before the final response, and a silent timeout appears as the sender's own timeout notice logged against the MX host.
When I see a 450 line, I let the scheduled attempt run; when I see repeated drops or timeouts on the same host, I check whether the failure follows one recipient domain instead of every domain in the batch. I also read the connecting IP and MX host because a timeout limited to one MX often points to that host rather than to my sending setup.
The receiving mail server is under load, rebooting, or in the middle of maintenance. That same message goes through cleanly on the next attempt unless the outage persists.
Policy and content deferrals
Greylisting is a deliberate deferral. The server sees an unfamiliar sender and refuses once to see if you'll retry. Real senders do; spam tooling doesn't. The 451 response carries a retry hint, so wait for the stated delay before the next attempt. Rate limiting is the volume cousin, and connection throttling looks the same: the receiving domain caps how fast you send or how many simultaneous connections you open, then pauses you. Both return 4xx signals tied to your sending behavior. The remedy is cadence or connection concurrency.
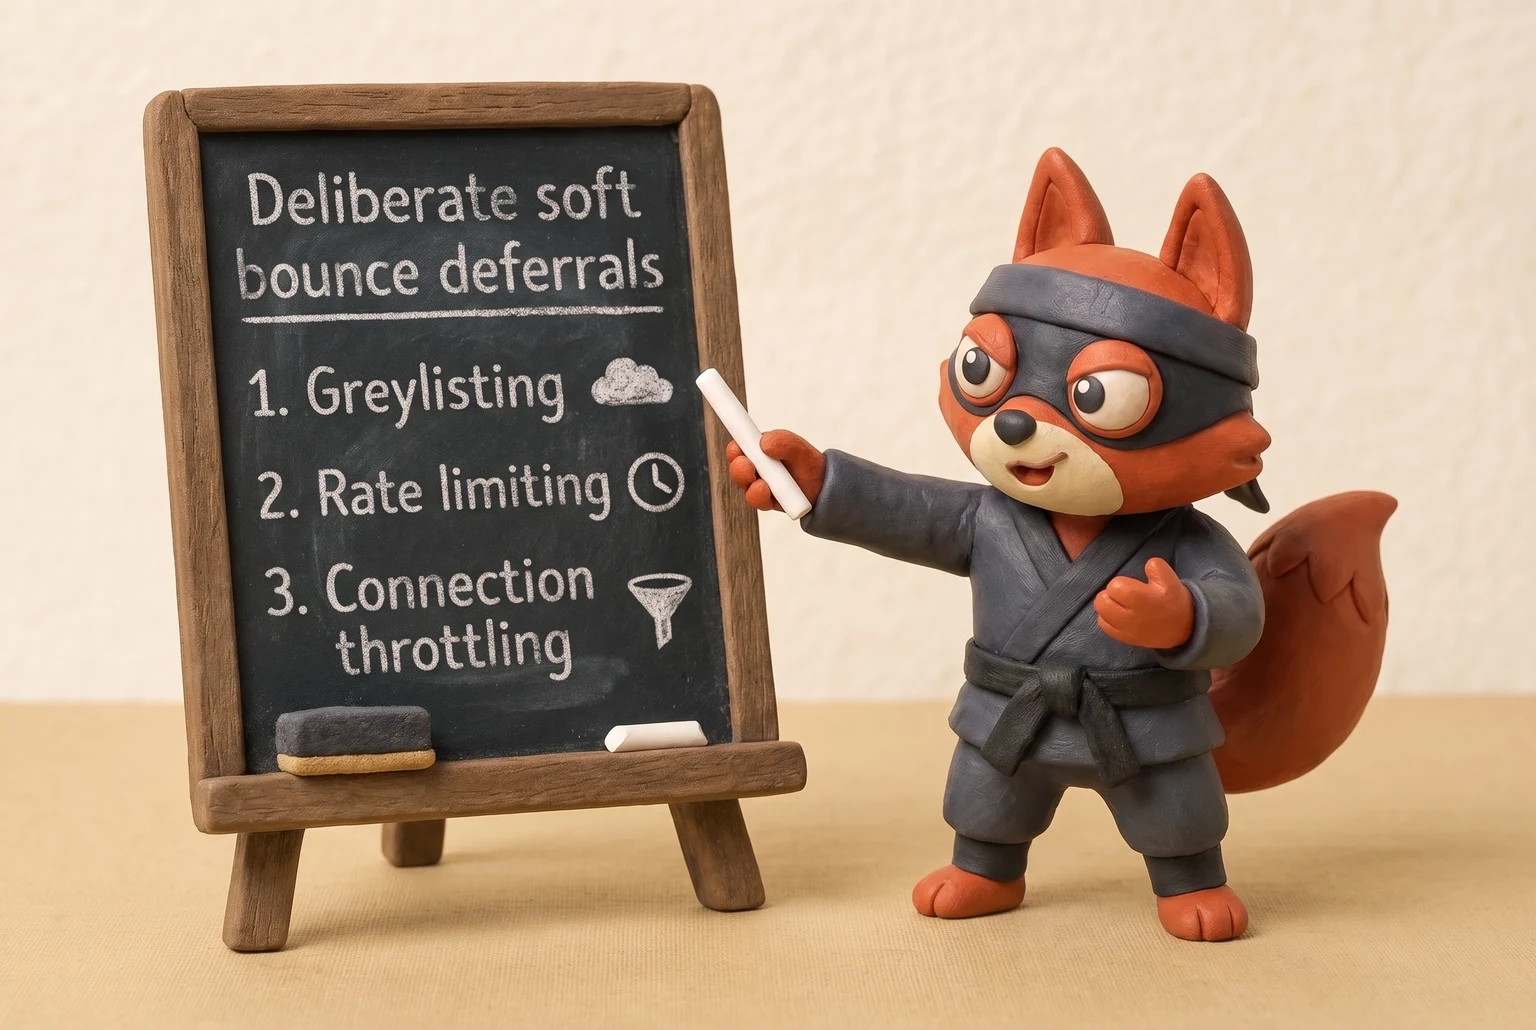
Field note: In the lists I clean, a 4.7.1 content deferral traces to a shared link pattern in the template; the addresses pass validation.
Content and spam filtering hides behind the 4.7.1 code. Link patterns, a naked IP address in the body, or a subject line that trips a filter can produce that deferral. The decision targets the content and leaves the recipient address clean.
Authentication failures
SPF, DKIM, and DMARC failures are the quiet cause. RFC 7208, RFC 6376, and RFC 7489 define those authentication standards.
When SPF doesn't list your current sending IP, or a forward breaks DKIM, a receiving domain with strict DMARC enforcement can defer the message while applying stricter checks. See Email Authentication Mechanisms: DMARC, SPF and DKIM. That deferral looks like a timeout in the bounce log.
Retrying won't fix a broken SPF record.
That split determines the fix: full mailboxes and timeouts clear on their own. Content filtering, greylisting, and authentication problems require a different move: change the content, slow the cadence, or fix the DNS.
Soft Bounce vs. Hard Bounce: How the Difference Changes Retry Logic
When I audit a client's list, the first thing I check is whether the bounce log actually separates 4xx replies from 5xx replies. If the ESP stuffs both into a single "bounced" column, you make every downstream list decision blind.
The 4xx/5xx split decides the action. You don't need a bounce label to tell you what to do; the first digit decides.
| Aspect | Soft bounce (4xx) | Hard bounce (5xx) |
|---|---|---|
| Server response code | 4xx: transient, try later (RFC 5321) | 5xx: permanent, no retry (RFC 5321) |
| Typical causes | Mailbox full (452), greylisting (451), server timeout or rate limit (450) | Mailbox not found (550), domain does not exist (550), invalid recipient (553) |
| Retry behavior | The ESP retries on a schedule, first within minutes, then at growing intervals | No retry; the address is dead |
| List action | Pause, retry; suppress after the 5-Deferral Rule | Remove immediately |
| Reputation impact | Repeated 4xx failures on the same address signal a list that nobody maintains | Each dead address sends an immediate negative signal to inbox providers |
Retry logic follows the code. Pause a 452 mailbox full and retry later. That mailbox may clear once the recipient deletes mail. Remove a 550 mailbox not found right now, because no retry schedule will bring that address back.
The hard rule I give every team: a hard bounce means remove immediately. A soft bounce means retry on schedule. Without a hard limit you will keep mailing dead addresses. Servers don't always tell the truth on the first pass. An address that returns 4xx for three, four, five campaigns running is probably not coming back.
Suppress it after five consecutive soft bounces under my 5-Deferral Rule, not after the first one. Neither reply is neutral. A hard bounce says the address is dead; a soft bounce says the address may be alive but unavailable. Retrying a valid but temporarily unavailable address is normal; keeping an address that 4xx bounces every campaign is a slow bleed.
Field note: The 5-Deferral Rule works for transactional streams, and for monthly newsletters I count the same five 4xx replies across a rolling one-year window because consecutive campaigns span a year. I set the window by send frequency.
I avoid tools that auto-remove an address after a single 4xx. I don't rely on Verifox or any paid API to distinguish a 452 from a 550; the reply code sits right in the bounce log and answers the immediate condition, while a paid API answers address status after the suppression rule has run. I need a suppression rule that respects the code, then a validation sweep later to catch the addresses that kept bouncing.
How Email Service Providers Handle Soft Bounce Email
Retry backoff by ESP
Your ESP's retry backoff isn't a waiting room. It's a reputation filter.
The first retry usually fires within minutes of a 4xx reply. The next attempt lands a few hours later. The final one sits a day or more out. SendGrid's bounce documentation (as of 2025) commits to retrying soft bounces for up to 72 hours before writing the address off as a permanent bounce. That window varies by provider and account tier. Amazon SES uses a shorter window, but the shape is the same: minutes, hours, days.
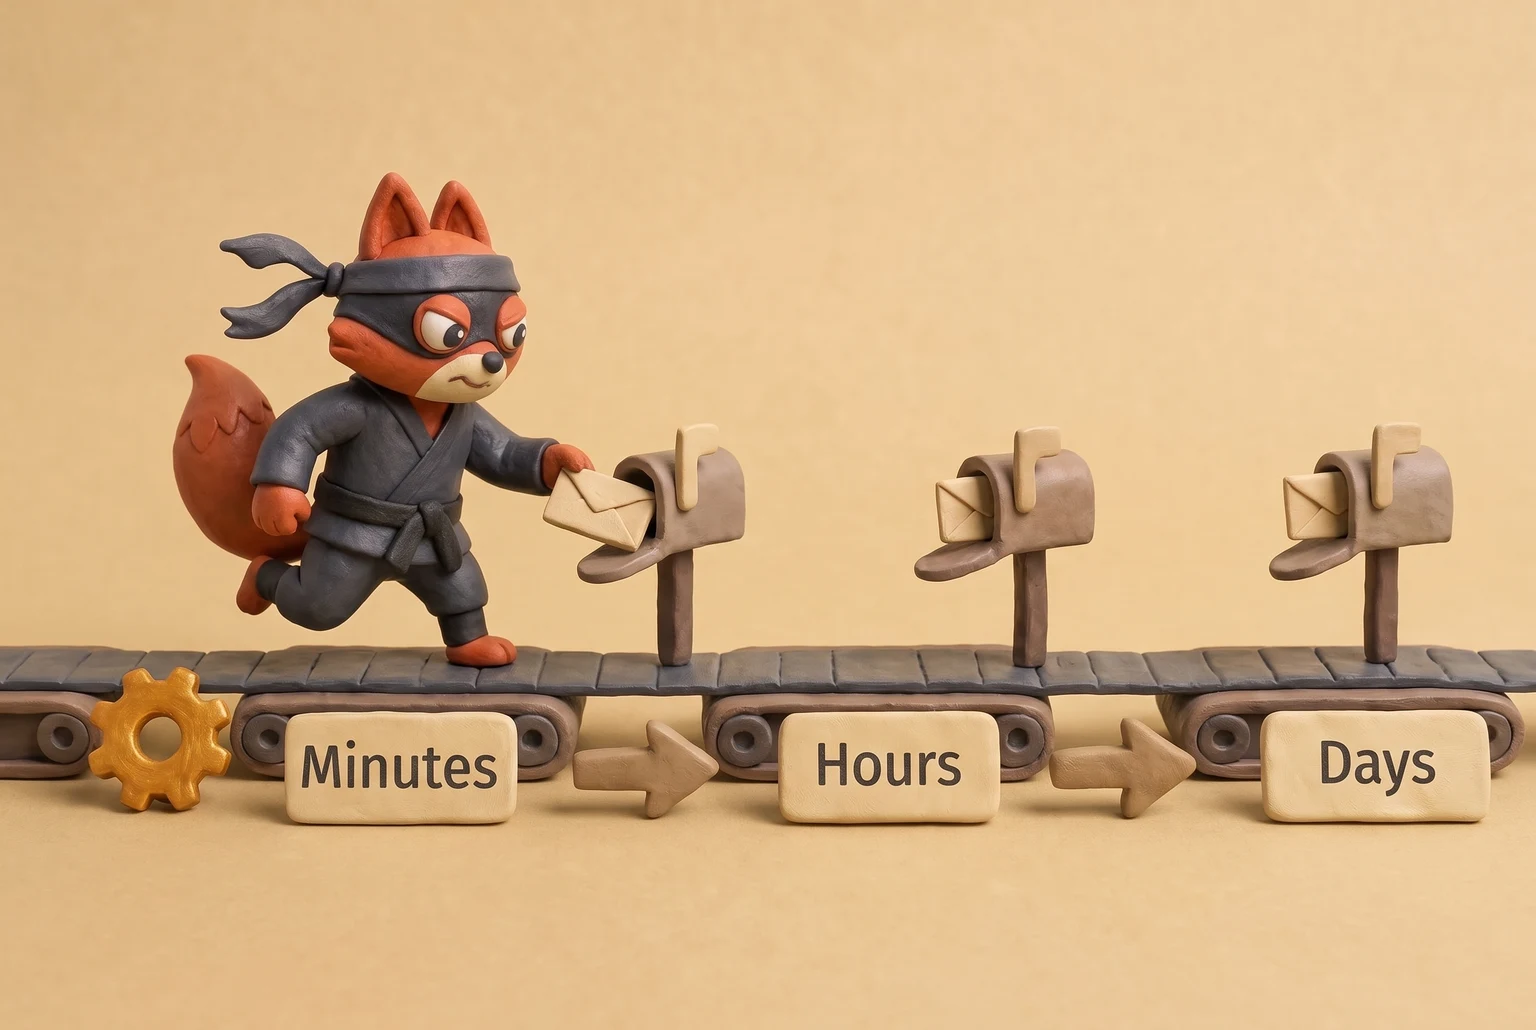
That schedule is deliberate.
An over-quota mailbox needs time to clear. A struggling server needs you to wait it out. Retrying every 30 seconds tells the receiving server "script," not "sender." The gaps get longer because the receiving server's greylisting window usually requires waiting out a set period, and a full mailbox might take a day to clear.
Suppression thresholds
Suppression thresholds sit after the retry schedule exhausts. MailerLite's documentation sets suppression at three consecutive soft bounces. Brevo's draws the line at five.
I keep this ESP comparison table date-stamped so the threshold claim stays citable:
| ESP | Retry window | Suppression threshold | Consecutive-campaign vs consecutive-retry counting | Source URL (last checked) |
|---|---|---|---|---|
| SendGrid | Up to 72 hours | Not stated in current article | Retry-based | docs.sendgrid.com |
| Amazon SES | Shorter than SendGrid | Not stated in current article | Retry-based | aws.amazon.com |
| MailerLite | Not stated in current article | Three consecutive soft bounces | Campaign-based | mailerlite.com |
| Brevo | Not stated in current article | Five consecutive soft bounces | Campaign-based | brevo.com |
| Postmark | Not stated in current article | Not stated in current article | Retry-based | postmarkapp.com |
| Mailgun | Not stated in current article | Not stated in current article | Retry-based | mailgun.com |
| SparkPost | Not stated in current article | Not stated in current article | Retry-based | sparkpost.com |
| Klaviyo | Not stated in current article | Not stated in current article | Campaign-based | klaviyo.com |
| HubSpot | Not stated in current article | Not stated in current article | Retry-based | hubspot.com |
| Constant Contact | Not stated in current article | Not stated in current article | Campaign-based | constantcontact.com |
Last checked: 2025. The threshold range matters because it's the point where one-off turns into recurring. One soft bounce during a holiday surge clears, leaves the address active, and causes no harm. The same address soft bouncing on every send for four months is dead weight your ESP will eventually quarantine.
The difference lives in your ESP's analytics. A single soft bounce event appears as a deferral, not a suppression candidate. A chain of consecutive failures flips the address into suppression. The threshold exists to catch addresses that never clear, not a one-time full mailbox.
Why three or five? The threshold reflects how long an ESP will vouch for a sender's list hygiene before its own IP reputation takes a hit. Every retry is a connection attempt to the same mailbox provider. If that provider repeatedly refuses the same address, it logs the pattern. A one-off soft bounce barely moves your bounce rate in ESP analytics.
A repeated soft bounce chain raises your bounce rate on the receiving domain, which feeds into the sender score that inbox providers assign. That's separate from spam complaints, but it still signals stale list data.
Why catch-all domains distort the verdict
Catch-all domains warp that verdict. A domain that accepts mail for any address never returns the 550 "no mailbox" code. So the ESP doesn't get the hard signal it needs. A 4xx from a catch-all domain is either a real mailbox with a full quota or a nonexistent address the domain accepts under its policy and then defers. In my cleanup work, catch-all domains are the usual suspect when a soft bounce never clears but the domain itself checks out.
Field note: A catch-all check costs nothing to reason about: if the domain accepts all, a 4xx soft bounce tells you almost nothing about the address. You need a separate address status check.
A single deferral is a delay; a recurring 4xx is a pattern you cannot ignore.
Read Bounce Codes to Diagnose a Soft Bounce Email
A bounce report that only says "soft bounce" or "soft bounce email" leaves you blind. The useful signal sits one layer down, in the SMTP reply and the enhanced status code attached to it. That combination tells you to wait, shrink the message, or repair authentication.
Start by reading the two-part code, because the first layer only narrows the problem. A log line like 452 4.2.2 Mailbox full carries an SMTP reply defined in RFC 5321: the server answered, but the mailbox refused the message right now. See SMTP Error Codes. The second part, 4.2.2, is the enhanced status defined in RFC 3463, and it names the exact condition: recipient mailbox full. That pair means wait. The address is valid.
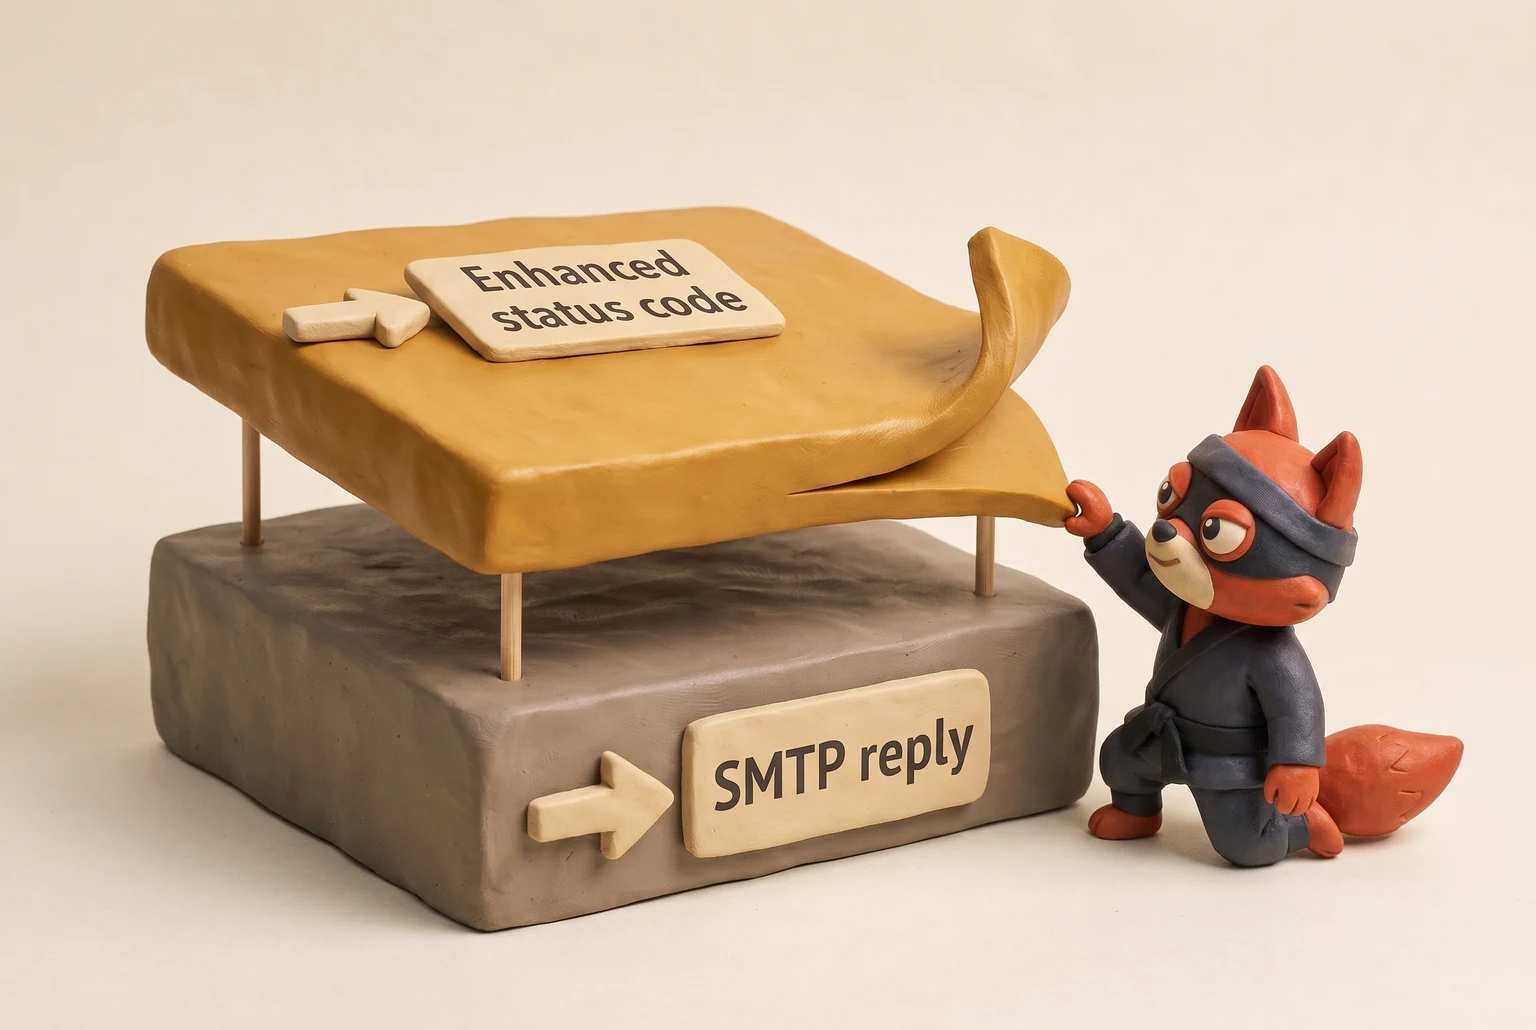
Enhanced status codes follow a class.subject.detail structure from RFC 3463. The first digit confirms temporary, the second names the component, the third specifies the condition. A 4.2.2 reads as temporary, mailbox, full. Once you learn the grammar, the dashboard's guess stops mattering.
450: Mailbox unavailable or greylisting
450 is the code you have to interrogate. RFC 5321 defines it as mailbox unavailable, but receiving servers also push greylisting through the same number. The retry hint separates them. A mailbox-unavailable 450 clears on the next attempt. A greylisting 450 expects you to honor the receiving server's deferral window; retry early and the clock resets.
Field note: When a receiving host reuses 450 for both cases, the diagnostic string's retry hint is the real separator. Read it before you suppress the address.
452: Full mailbox vs. message too large
452 covers two conditions that dashboards tend to merge: insufficient storage and message too large. The enhanced status splits the fix for you. 452 4.2.2 signals a full mailbox, so wait for the recipient to delete mail. 452 4.2.3 signals that message length hit an administrative limit, so shrink the attachment and resend. Retrying the same oversized file produces the same bounce every time.
421: Service not available or IP throttling
421 changes the target. RFC 5321 classifies it as service not available, and receiving hosts use it for connection refusal under load or deliberate IP throttling. That's a sending-cadence problem: slow the stream, cap simultaneous connections, and let the retry schedule run. If the deferrals continue after adjusting cadence, check your sending volume against the receiving domain's published limits.
451: Temporary policy or authentication deferral
451 is the policy counter. It means the server refused the transaction for a temporary policy or authentication reason, separate from the mailbox state. Greylisting hides here, and so does a domain that defers messages because SPF or DKIM failed. When one domain keeps deferring addresses that look fine, check authentication before you touch the list. In the lists I clean, that check surfaces the real culprit faster than removing contacts ever does.
If your ESP dashboard flattens every 4xx into one "deferred" bucket, export the raw delivery event. Look for smtp_response or delivery_status in the exported file: that string is where the real diagnosis lives.
4.7.1 is the code that gets misread. It signals content policy: a link pattern, a naked IP address, an attachment type, a subject line that tripped a filter. The address passes validation. Edit the template; leave the contact alone.
The code decides the move.
A throttled 421 or 451 points at your sending setup. 452 4.2.2 points at the recipient's mailbox. 452 4.2.3 points at file size. 4.7.1 points at the template. The dashboard calls all of them the same soft bounce email. The log tells you which one to fix first.
Automate Soft Bounce Email Management With a Validation API
Attach a validation call to the email verification API docs from the bounce webhook you wired using the bounce webhook wiring tutorial instead of sorting 4xx replies by hand. RFC 5321’s 451 says “not now,” not whether the local part exists. A paid API earns its cost at this decision point. If all you want is MX and syntax checks, skip the paid service and query DNS records yourself.
async function validateAfterSoftBounce(email) {
 const apiKey = process.env.EMAIL_VALIDATION_API_KEY;
 const response = await fetch(process.env.EMAIL_VALIDATION_ENDPOINT, {
 method: 'POST',
 headers: {
 'Authorization': `Bearer ${apiKey}`,
 'Content-Type': 'application/json'
 },
 body: JSON.stringify({ email })
 });
 const data = await response.json();

 // {
 // "status": "invalid" | "risky" | "valid",
 // "sub_status": "mailbox_full" | "disposable" | "role_account",
 // "mx": true,
 // "smtp": true,
 // "catch_all": false,
 // "checks": { "syntax": true, "mx": true, "smtp": true, "catch_all": false }
 // }

 if (data.status === 'invalid' || data.checks.smtp === false || data.checks.mx === false) {
 return { action: 'suppress', reason: data.status };
 }

 if (data.catch_all === true && data.sub_status!== 'mailbox_full') {
 return { action: 'suppress', reason: 'catch_all' };
 }

 if (data.status === 'risky' && data.sub_status === 'mailbox_full') {
 return { action: 'retry', delayHours: 24 };
 }

 return { action: 'retry', schedule: 'esp_retry_window' };
}
This branch decides on the validation status, not the bounce label. The response fields that drive the branch are 'status', 'checks.smtp', 'checks.mx', 'catch_all', and 'sub_status'.
A 451 with an invalid status or a failed SMTP/MX check suppresses now; a 451 from a catch-all suppresses unless 'sub_status' is 'mailbox_full'; a 451 or 452 with 'mailbox_full' retries after 24 hours; every other 4xx deferral retries on the ESP schedule. An invalid status or a failed SMTP or MX check suppresses now, even when the original code was a 451.
A catch_all result suppresses an unknown local part unless the mailbox itself reported full: the domain accepts the address, yet the soft bounce says nothing arrived. A risky mailbox_full address gets a 24-hour pause, so the ESP’s retry window clears the quota instead of hammering it. The generic retry falls back to the ESP schedule, so the code never hardcodes a six-hour guess.
Field note: The catch_all flag separates a real quota problem from a domain that accepts any local part and defers the unknown. Without it, a 451 on a catch-all domain looks identical to a 451 on a live mailbox.
Those four outcomes cover every 4xx reply that reaches the webhook: a dead address, an unresolvable catch-all, a full mailbox, and a deferral the ESP should handle.
Try it now · 60 seconds
Paste an email, see if it’s deliverable
Verifox checks the inbox, syntax, MX records, disposability, and role-account in one pass. Free, no signup needed for the first check.
No card required · 1,000 free credits at signup (2,500 work email) · 99.99% accuracy
Email Address Status Glossary for Soft Bounce Triage
A soft bounce is a delivery event, not an address label. Pair the SMTP code with Verifox's status before you choose retry or suppress. The status tells you whether the 4xx points at a fixable condition or a dead end. See RFC 5321, Simple Mail Transfer Protocol.
| Status | What it means for the soft bounce decision |
|---|---|
| Valid | The mailbox exists and tests passed. Retry on the ESP schedule; the 4xx was likely transient. |
| Invalid | SMTP or MX check failed. Suppress now; the 4xx may hide a dead address behind a catch-all or stale domain. |
| Risky | Check sub-status: mailbox_full → pause and retry after 24h; greylisting → honor the server's retry hint. |
| Catch-all | The domain accepts any local part, so a 4xx does not prove the mailbox exists. Suppress unless sub-status is mailbox_full. |
| Disposable | A temporary address that will soon stop receiving. Suppress; it inflates bounce rate. |
| Role-based | Shared inbox (sales@, info@) that fills faster. Retry, but flag for early suppression if 4xx recurs. |
| Unknown | The API couldn't confirm the address. Require retry or additional validation before a decision. |
The Risky bucket is where sub-statuses earn their keep. A mailbox_full is a capacity problem that clears; a greylisting is a deliberate deferral expecting you to honor the retry window. Treat them as separate conditions.
The bounce code names the immediate condition; the status names the address quality. Merge both before you click suppress.
Field note: An Unknown status on a 4xx is the one case where I let the ESP's own retry window run before touching the contact.
How to Reduce Soft Bounce Email Without Burning Sender Reputation
Fix data collection before you touch send frequency.
Cutting send cadence to chase a lower soft bounce rate is backwards. Skip aggressive frequency changes as a first fix. A throttled stream may reduce 421 and 451 deferrals, but it won't fix a list full of typo addresses, dead inboxes, and dormant accounts. Aggressive frequency changes also cut engagement from active subscribers, which weakens the positive signal that keeps you out of spam folders.
Double opt-in belongs at the signup form, before any other cleanup step. The confirmation email carries a single-use link; a typo in the address never completes the click, so the bad address never enters the list. That catches the most common data-entry errors before the first campaign and keeps bot-submitted addresses from populating the list with future soft and hard bounces.
Run a validation sweep before campaigns, before the bounce report arrives. A validation API checks RFC 5322 syntax, queries MX records per RFC 1035, and opens an SMTP handshake to verify the mailbox accepts mail. See RFC 1035: Domain names.
It also flags catch-all domains and disposable addresses before you spend retry attempts on them. A validation sweep suppresses dead domains and invalid mailboxes before they burn the ESP's retry queue. Purchased B2B data carries a 2-4% soft bounce rate; a double opt-in B2C list runs under 1%.
Read that gap as a data-quality verdict, not an ESP deliverability failure.
Segment by engagement before every send. ZeroBounce's published list decay study found about 28% of an average list decays each year. A contact who hasn't opened in a long stretch is more likely to have a deactivated or recycled mailbox, so send the regular campaign to the engaged segment. For the dormant segment, run validation or a re-engagement campaign with a clear unsubscribe link. Don't keep mailing dormant addresses at full frequency.
Keep the message itself from triggering size-based soft bounces. Keep HTML weight under 100 KB. A receiving mail server that advertises a SIZE limit returns 452 4.2.3 when the message exceeds it, and bloated templates with embedded images or tracking scripts are the usual trigger. Avoid aggressive attachments: a heavy PDF deck attached to a cold email is a reliable path to that 452 or a content deferral. Put large files behind a link instead.
Field note: In the lists I clean, the lowest soft bounce counts come from clients who never let a dirty list reach the ESP. They validate first, double opt-in second, and the bounce report stays boring.
Fix collection and list hygiene first, and let the ESP's retry and suppression schedule do what it was designed to do.
Soft Bounce Email FAQs
How many soft bounces before it becomes a hard bounce?
Your email service provider's suppression threshold sets the limit, and most publish it. Read that page: many ESPs stop retrying an address after several consecutive failures, and some count consecutive campaigns instead of individual retries. If an address soft bounces on several consecutive sends, remove it yourself before the provider does.
Does a soft bounce mean the email address is invalid?
No. A soft bounce means the address could not receive mail at that moment. A full mailbox, a busy server, or a temporary deferral all happen on valid addresses. A hard bounce carrying "mailbox not found" or "user unknown" is permanent. Watch for repeated soft bounces on the same address at a catch-all domain. That pattern can hide a dead address, so verify the mailbox before you keep mailing it.
Will Gmail retry soft bounces?
Yes, on the sending side. Google Workspace and Gmail retry deferred messages from their outgoing servers, so you configure nothing. When you send to a Gmail mailbox, your own sending service manages the retries until the temporary condition clears; the mailbox accepts the message once the inbox has space or the deferral ends.
Can SPF, DKIM, or DMARC cause soft bounces?
Yes. Authentication failures on your end produce a deferral on theirs. A sending IP missing from your SPF record, or a forward that broke DKIM, gives a strict DMARC domain a reason to hold the message and run additional checks. The result lands in your bounce log as a soft bounce while the address itself tests fine. Fix it in DNS, not in your recipient list. Update SPF to include every sending source, then retest before suppressing anyone.
How do I stop soft bounces in Mailchimp or other ESPs?
Mailchimp and other ESPs already retry soft bounces and suppress addresses after repeated failures. The part you control is list hygiene. Clean the list before you send: require a confirmation click at signup, validate contacts that have sat untouched for a year or more, and route dormant addresses into a separate reactivation series instead of the main send. That clears out the full mailboxes, dead domains, and catch-all traps behind most soft bounces. Lowering send volume first hides the data problem rather than fixing it.
Fix Soft Bounces Before They Become Hard Bounces
A repeated 4xx reply to the same address forces my ESP to retry that address on every campaign until I suppress it. The decision I make after a soft bounce is whose retry policy controls my list: the receiving server's or my own repeat threshold. The rule I enforce on every marketing list: suppress the same address after five consecutive soft bounces. Five matters. Your ESP retries a deferred message more than once, then drops it. If the same address bounces soft on five separate sends, the condition survived each retry batch. That is persistent failure.
When a 452 clears after two hours, the inbox came back from the weekend. When the same 452 greets you on five separate campaign sends, the inbox is not clearing. Leaving suppression to my ESP's automatic threshold lets the receiving server's retry policy shape my domain reputation before the address is removed. Manual suppression removes the address before that threshold, which usually comes later and counts against my account. Manual suppression at five keeps you in control of the list, not the receiving server.
In January 2026 I audited a 41,000-record list for a B2B fasteners distributor. One shared purchasing inbox returned 452, mailbox full, on nine consecutive campaign sends. See Gmail SMTP errors and codes. The sales team kept the address active because "it's a customer." It had not accepted a message in six weeks. The list owner suppressed it at five, then ran a Verifox validation check.
The API marked the address deliverable, but the webhook history showed the same 452 for every attempt. The condition was real, not a typo. Suppressing at five saved the ESP from burning retry cycles and kept the sender's domain from logging repeated deferrals.
Pair the code with a validation API check for any soft bounce email. The code names the immediate condition: 4.2.2 means full mailbox, 4.7.1 means throttle. The API names the address quality: valid, disposable, unknown, role account. If the code says 4.2.2 and the API says valid, wait and retry. If the code says 4.7.1 and the API says unknown, suppress and remove.
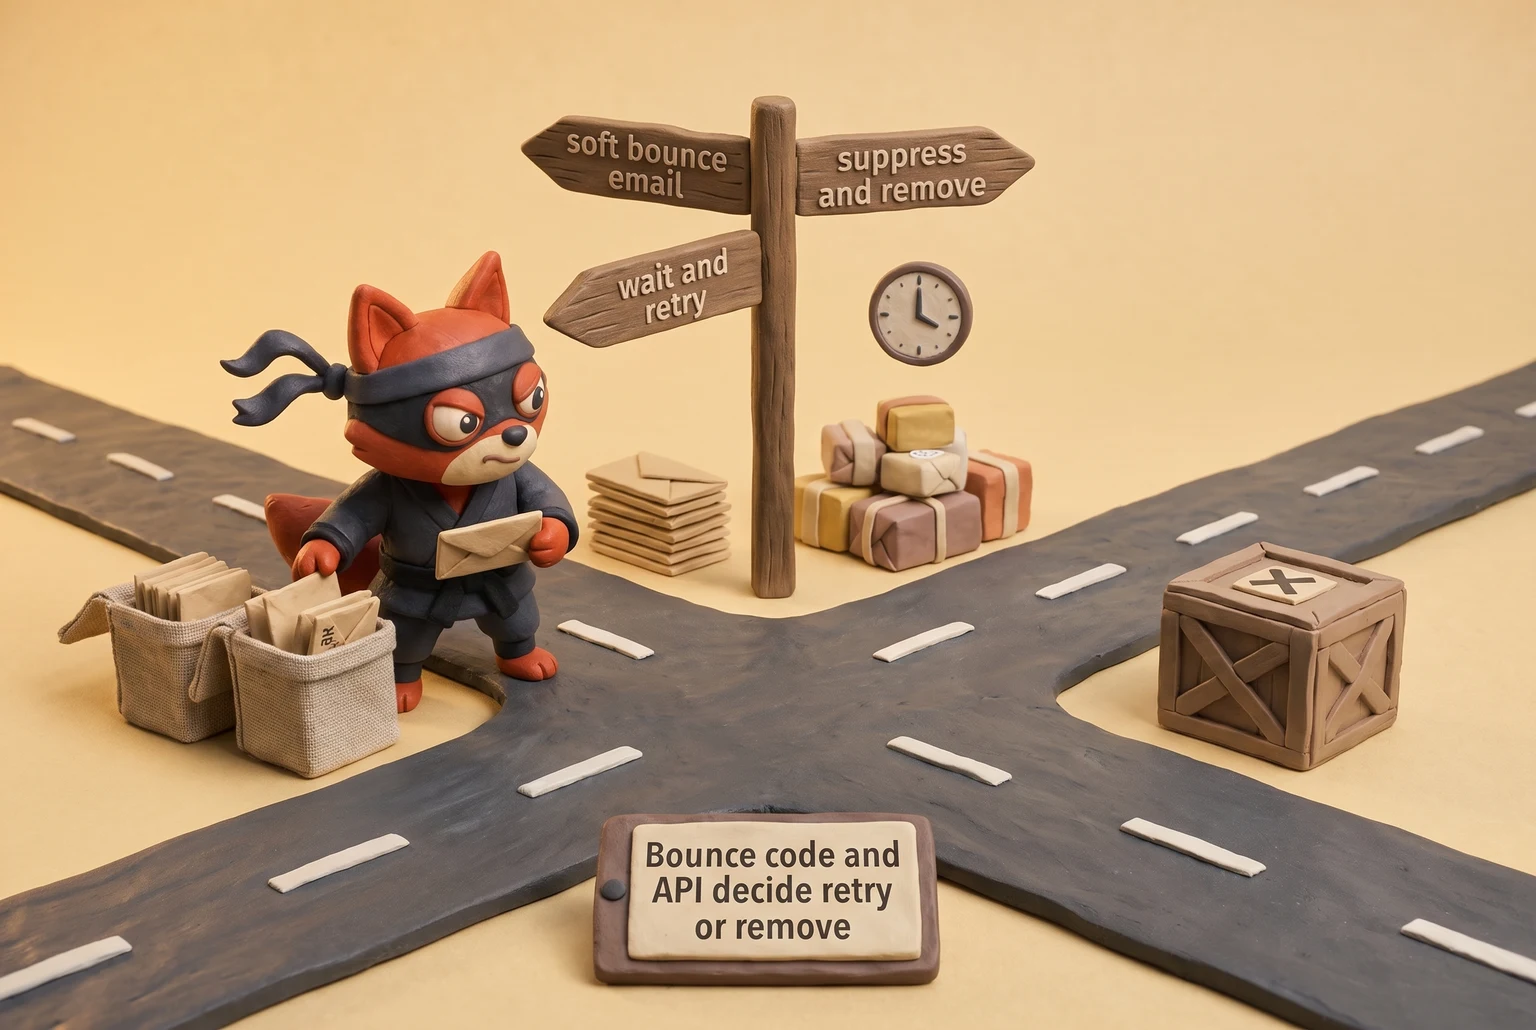
That order suppresses dead weight before the ESP does. Reduce soft bounce email volume by validating before send and retrying intelligently after bounce. Try Verifox's validation API on your next bounce webhook and start my validation run.
Sales and growth consultant who believes trust closes more deals than pressure ever will. Nearly five years at Turnix in New Delhi. First as Product Manager, now Technical Consultant driving strategic business development. Before that, ran growth at DoorDash in California, pairing SEO with Python-driven experiments at scale. MBA from Stanford. Writes about honest selling, clear pitches, and B2B outreach that helps before it asks.