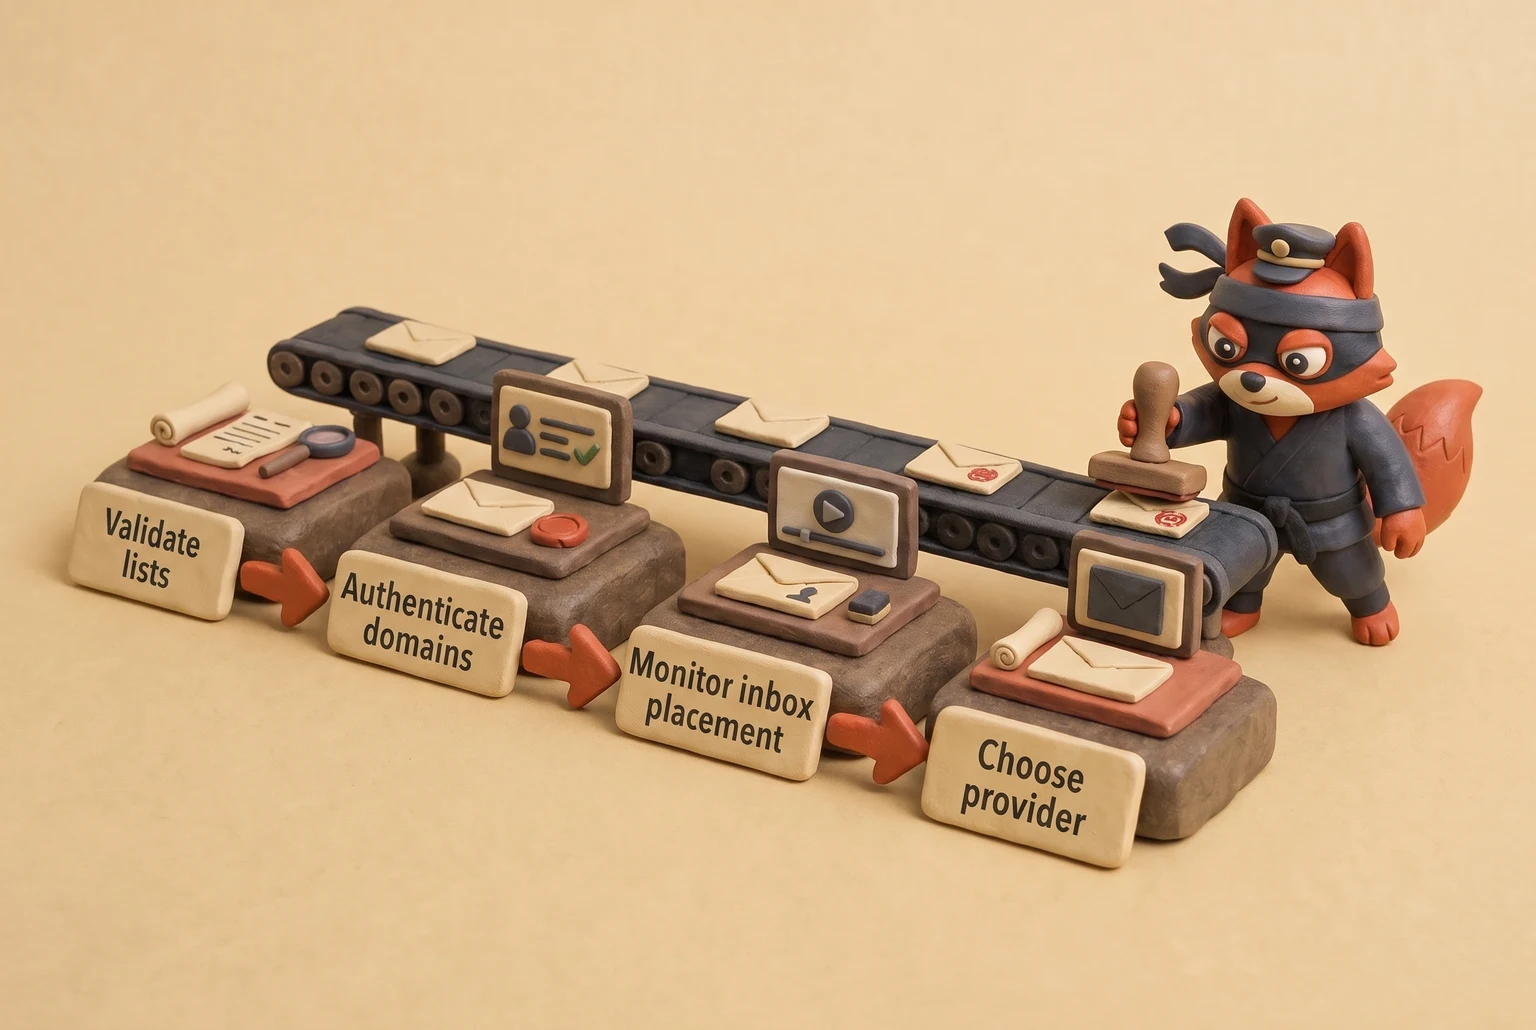
Your sender score survives only if you validate before send, authenticate DNS, and monitor seed placement quarterly. Pick a provider that supports that workflow, not the one with the best feature grid. Validate at the point of capture, enforce the seven statuses, and no provider can save a stale list.
Email Delivery Service: The Short Answer
Most email delivery service failures come down to five root causes: unvalidated lists, DNS misconfigurations, a shared IP's noisy neighbors, content that trips spam filters, and sudden sending volume changes. Unvalidated lists introduce hard bounces that tank your sender score. DNS records like SPF and DKIM are easy to get wrong, leading to authentication failures.
Shared IPs can have their reputation poisoned by other senders. Spammy-looking content gets flagged by inbound filters. And a sudden spike in sending volume from your domain can look like a compromised account to a mailbox provider, landing your mail in the spam folder. An email delivery service is the infrastructure provider that sends your mail via an API or SMTP relay.
Choosing one starts before you compare provider rankings, pricing tables, and DNS authentication checklists. Provider features look identical on a feature grid; the difference shows up in your bounce logs.
The real question is whether the service has validation and deliverability controls that protect your domain from day one. Most guides skip the validation layer, so they miss the decision that actually matters. Switch vendors without fixing the list and the first thing a new provider delivers is a queue of hard bounces. I took a 2 a.m. page because a list nobody validated tanked a domain's sender reputation.
This post unpacks the list-validation and DNS-authentication failure modes and shows you how to fix them at the source, starting with the Verifox validation layer. That page was for a 50% hard bounce rate on a new campaign, and the fix wasn't a new IP address-it was deleting 40,000 unvalidated addresses from their list.
TL;DR: An email delivery service is transport infrastructure. It accepts mail and returns RFC status codes, but a 250 accepted is not an inbox placement.
- Use the Validate-Audit-Monitor (VAM) loop: Hard bounces, catch-alls, disposables, and role addresses are separate failure modes a delivery provider won't screen for you.
- Choose the integration by workflow: SMTP relay for drop-in compatibility, REST API for idempotency, structured errors, and per-recipient webhooks.
- Rank providers after the workflow: Amazon SES is cheap raw infrastructure, Postmark is curated deliverability, Resend is developer experience, SendGrid is enterprise integrations, Mailgun is pay-as-you-go.
- Protect sender score with DNS authentication and monitoring: SPF, DKIM, DMARC at quarantine or reject, and seed list checks before switching vendors.
What Is an Email Delivery Service?
The transport layer does not build lists, design campaigns, or clean bounces. It accepts mail over SMTP or a REST API, resolves MX records (RFC 1035), and returns RFC 5321 status codes like 250 accepted or 550 no mailbox.
See RFC 1035: Domain names. That layer is infrastructure. For example, when I route a client batch through a delivery service, I am only checking that each recipient domain resolves and that the receiving server returns an accept or reject status; the service never builds audience segments, designs the email template, or decides which addresses belong on the list.
Another boundary: a delivery service will attempt delivery to a catch-all or disposable domain unless a separate validation step screens that address first.
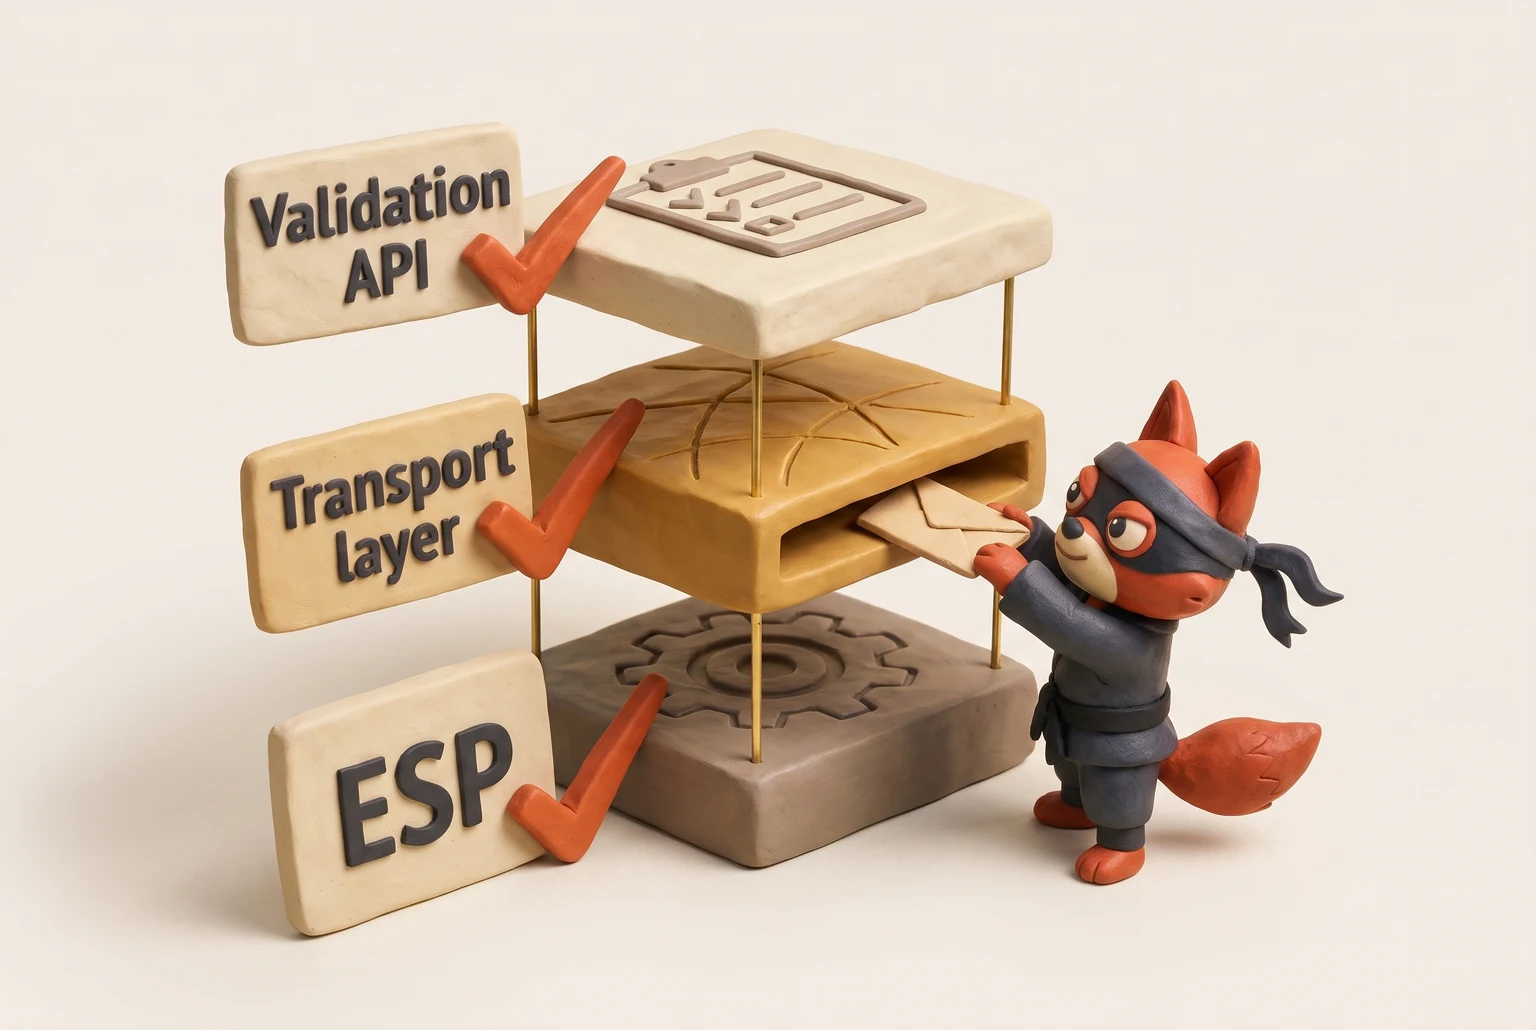
Mailchimp-style email service providers (ESPs) sit above it. They orchestrate campaigns, lists, and scheduling. A validation API like Verifox does a third, earlier job: it screens catch-all and disposable domains before the transport layer touches them. When I'm cleaning a list for a client, I treat those as three separate machines. Choose the delivery layer on its own. A weak list burns any transport you buy. Key takeaways: I run a Validate-Authenticate-Monitor loop.
- Validate: I screen every address through a verification API before the transport layer touches it, removing catch-all and disposable domains first.
- Authenticate: I configure SPF, DKIM, and DMARC on the sending domain so receiving servers trust the delivery service.
- Route: I send the cleaned list through the delivery service and read RFC 5321 status codes such as 250 accepted or 550 no mailbox.
- Separate: I keep the ESP and transport layers split so the ESP builds lists and campaigns while delivery only resolves MX records and returns accept or reject status.
- Monitor: I watch reject patterns by domain, then feed them back to validation before the next send.
Rather skip ahead? Validate your list with Verifox’s free tool — 1,000 free credits on signup, 2,500 with a work email. No card required.
Why Email Delivery Services Fail Without Validation
Most people assume delivery starts the moment you integrate a provider. That's backwards.
Your email delivery service is the courier, not the doorman. It carries the message to the receiving server and reports the server's answer. A 250 means the server accepted the message, not that the message landed in the inbox. Garbage addresses still get that yes. If your list contains addresses that never opted in, or contacts who abandoned those inboxes years ago, you're paying to hand those addresses to Gmail and Yahoo, where they become a liability.
That decay is real and measurable. Contacts leave jobs, abandon inboxes, or change domains. Each of those stale addresses becomes a bounce or a trap if you keep sending.
Google and Yahoo enforce bulk-sender rules that make this liability quantifiable. Gmail senders pushing 5,000 or more messages per day must authenticate See Email sender guidelines. with SPF and DKIM, publish a DMARC policy, include a one-click unsubscribe, and keep reported spam below 0.3 percent (Google's published threshold).
Yahoo's published guidelines require the same authentication, DMARC, unsubscribe control, and a low complaint rate. Invalid addresses drive bounces that signal list neglect. Spam complaints from recipients who never recognized your brand push you over the complaint benchmark, and then providers throttle your whole domain.
Problem 1: Hard Bounces
The bounces aren't the worst part. Hard bounces are loud; they come back as 550 no mailbox, and you can see them. The silent decay comes from catch-all and disposable domains. A 550 response means the mailbox does not exist. A 551 response means the local part is invalid at that domain, and a 553 response means the mailbox name is not allowed.
A 552 response flags an over-quota mailbox; some receiving servers treat it as temporary, but repeat 552s signal an address I should suppress. After one hard bounce, I block the address from the active send list. If the same address fails again in a later campaign, I quarantine it permanently so it never consumes another send.
That suppression step is what stops a dead address from becoming a repeated signal of poor list hygiene.
Problem 2: Catch-All Domains
A catch-all domain accepts mail for any local part. Type the address wrong, use a stale contact, or guess a pattern like [email protected], and the message still gets a 250 accepted response. No bounce. Nobody may monitor the address, or it may be a recycled spam trap. Spam traps are addresses that never signed up for anything; mailbox providers use them to catch senders who scrape or buy lists. Hitting one is a strong negative signal.
Problem 3: Disposable Addresses
Disposable addresses are worse in their own way. A user creates one for a single signup and then never checks it again. The first send reaches a real inbox; the next send bounces or the provider tags it as unwanted. Either way, your engagement metrics drop without a single explicit alert.
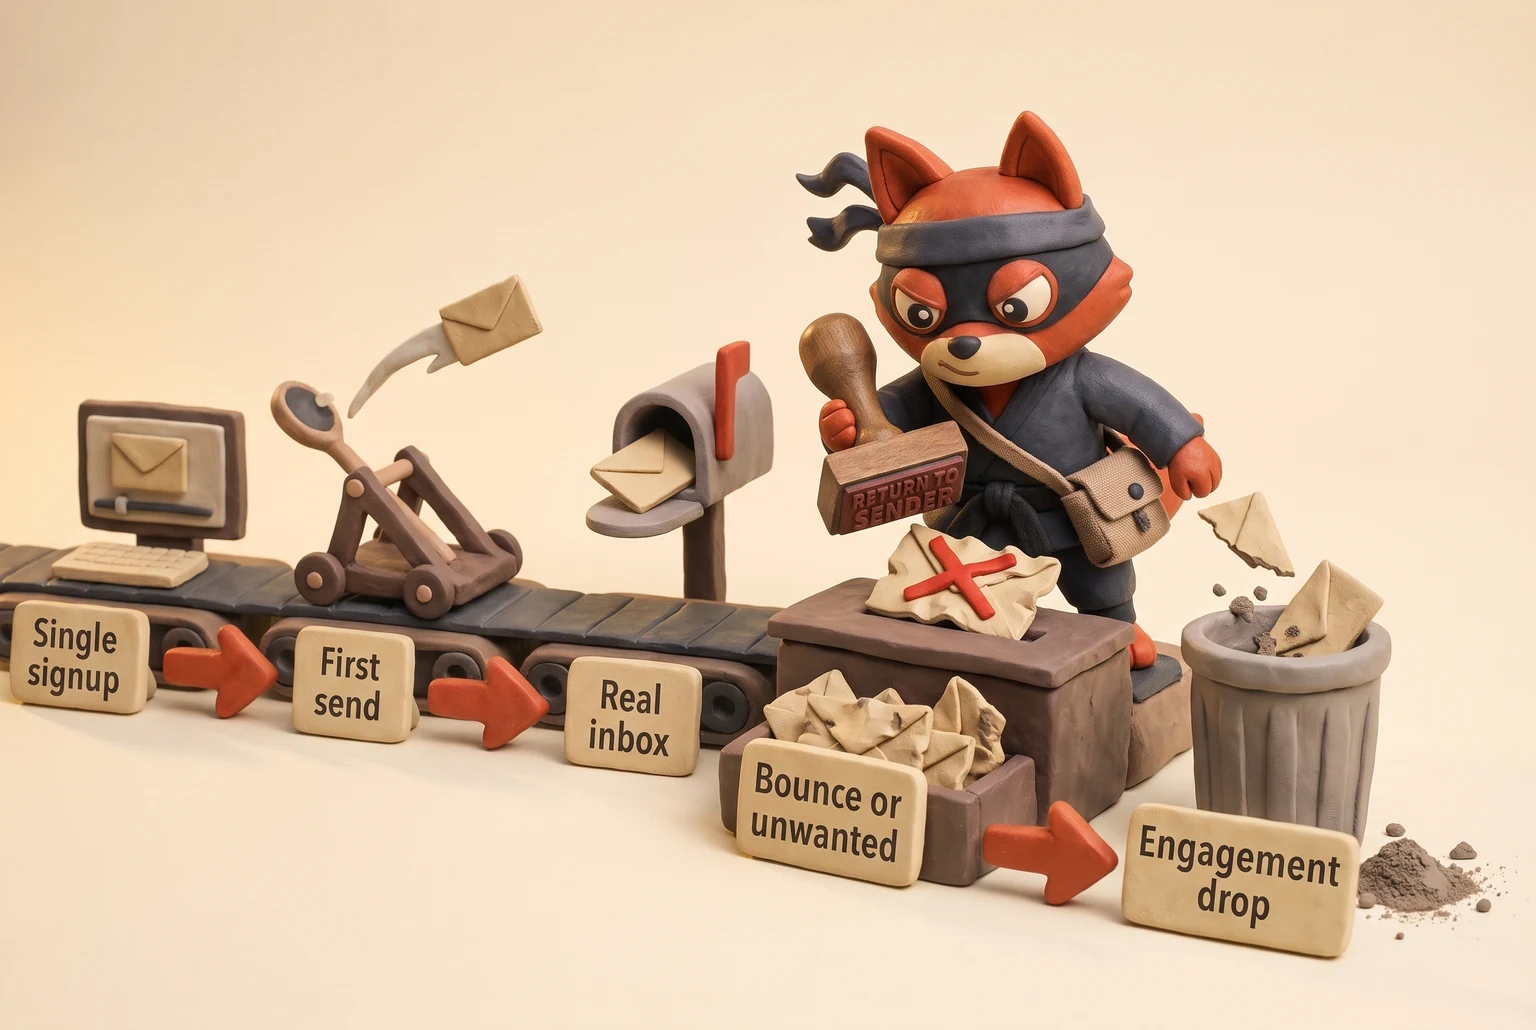
When I audit a B2B list, catch-all domains are where invalid addresses hide. A hard bounce tells you a mailbox is dead. A catch-all tells you nothing, which is worse.
That's why validation must come first in the workflow. A validation API checks syntax and MX records, flags catch-all or disposable domains, and returns a verdict before you spend a send. Verifox returns a machine-readable status for each address, so you can strip the bad ones from the batch and hand a clean list to your delivery provider.
That's the order that protects your sender score: reject first, then send.
I ran a validation pass over a client's B2B list and watched catch-all domains accept mail that hard bounces would have flagged.
Email Delivery Service Provider Rankings: The 2026 Shortlist
I've watched a bounce show up three sends later, after the damage.
Provider choice is workflow-specific, not universal. Mailgun sits between them for teams that want pay-as-you-go without deep infrastructure work.
Public list rates below, before volume discounts and negotiation. Verify each pricing page before you commit.
| Service | Best for | Free tier | Price per 1,000 at 50K / 1M | Dedicated IP option | Key tradeoff |
|---|---|---|---|---|---|
| Amazon SES | High-volume developers inside AWS | 62,000/mo first year | ~$0.10 / ~$0.10 | Yes, add-on | Raw infrastructure, no guardrails |
| Postmark | Curated, high-trust transactional mail | 100/mo | ~$1.25 / ~$0.85 | Yes, higher plans | Premium price per send |
| SendGrid | Enterprise integrations and marketing APIs | 100/day | ~$0.40 / ~$0.30 | Yes, Pro plan | Shared IP pool can swing reputation |
| Resend | Developer experience, modern API | 3,000/mo | ~$0.40 / ~$0.30 | Yes, higher tiers | Smaller ecosystem, fewer prebuilt plugins |
| Mailgun | Pay-as-you-go flexibility | 5,000 trial, then pay-as-you-go | ~$1.00 / ~$0.80 | Yes, add-on | Support tier jumps with contract |
Amazon SES
Best for high-volume developers who can wire their own infrastructure. Pros: lowest per-email cost, tight IAM, S3, and CloudWatch integration, no upfront commitment. Cons: no hand-holding; DKIM, SPF, DMARC setup and bounce parsing are on you. Ideal use case: transactional email for a SaaS platform already inside AWS that has an engineer who likes building.
Postmark
Best for teams where inbox placement is non-negotiable. Pros: curated shared IPs, strict onboarding, sender reputation controls that actually work, clear bounce and complaint handling. Cons: expensive per message at scale. Ideal use case: password resets, receipts, and B2B notifications where a single missed inbox costs more than the send.
SendGrid
Best for enterprises that need prebuilt integrations everywhere. Pros: deep plugin library, marketing and transactional split, strong Twilio ecosystem. Cons: shared IP pools can inherit neighbor reputation; deliverability swings unless you pay for a dedicated IP. Ideal use case: an enterprise team already standardized on Twilio that needs one vendor for both marketing and transactional mail.
Resend
Best for developers who want a clean REST API and no legacy cruft. Pros: excellent TypeScript-first SDK, webhook simplicity, modern dashboard. Cons: fewer prebuilt integrations, smaller community relative to SendGrid. Ideal use case: a new product where the backend team picks the stack and values API ergonomics over brand recognition.
Mailgun
Best for teams that want pay-as-you-go without long contracts. Pros: flexible pricing, strong SMTP relay, decent deliverability when configured correctly. Cons: shared IP quality varies, premium support locked behind higher plans. (Skip this one if you're a low-volume sender with a small list and no deliverability engineer; the shared pool risk isn't worth it.) Ideal use case: a mid-volume app that needs burst sending and prefers operational spend over monthly minimums.
Field note: The price column hides the real cost. A cheap provider with no suppression list management doubles your bounce cleanup time later, and that labor costs more than the per-email delta.
The rankings shift once validation enters the workflow. A clean list makes SES and Resend far safer; a dirty list makes even Postmark's curated deliverability a temporary shield. Pick the workflow first, then shortlist the provider against it.
Email Delivery Service Pricing at 50K, 100K, and 1M Emails
Per-thousand pricing is the base fare, not the ticket. At 50K, 100K, and 1M monthly sends, the cost you actually feel comes from dedicated IPs, support tiers, and throughput caps. Which line item actually moves your deliverability?
It's not the per-email rate.
| Provider | Free tier | 50K/mo est. | 100K/mo est. | 1M/mo est. | Dedicated IP |
|---|---|---|---|---|---|
| Amazon SES | 62,000/mo first year (EC2 sends) | ~$5 | ~$10 | ~$100 | Add-on |
| Postmark | 100/mo | ~$65 | ~$115 | ~$875 | Add-on |
| SendGrid | 100/day | ~$20 | ~$45 | ~$300 | Add-on |
| Resend | 3,000/mo | ~$20 | ~$40 | ~$300 | Add-on |
| Mailgun | 5,000 trial, then pay-as-you-go | ~$50 | ~$100 | ~$800 | Add-on |
I pulled these estimates from each provider's published pricing page (Amazon SES, Postmark, SendGrid, Resend, Mailgun), then rounded to the nearest $5. Verify each provider before you commit.
The free tiers hide the first trap. Amazon SES gives a huge first-year buffer, but only for EC2-sent mail. Postmark's 100 messages a month is a tasting portion. See The Amazon SES Free Tier. Resend's 3,000 free messages is enough to test an integration, not run a business. SendGrid's 100 per day sounds fine until a password reset wave hits at 9 a.m.
That's where throughput caps bite. A provider quotes a monthly volume but caps how many messages you can push per hour or per day. At 50K monthly sends, you rarely notice. At 1M, a 50,000-per-day cap means you pace sends over three weeks, which breaks time-sensitive transactional mail. Ask for the per-hour and per-day ceiling before you sign.
Dedicated IPs are the second line item nobody budgets for. Shared IP pools are cheaper and fine for low volume, but at 100K monthly sends you inherit the reputation of every sender on that pool. One spam wave from a neighbor and your domain warms up in the penalty box.
Dedicated IP add-ons cost about $25 per IP per month at Amazon SES, $30 at SendGrid, and $59 at Mailgun, per each provider's pricing page as of Q3 2023. Postmark charges for dedicated IPs as a separate add-on.
Resend bundles them at higher tiers or charges north of $100 per IP.
The line item that changes your decision is the dedicated IP, because a shared pool puts your domain next to senders you didn't vet.
Support is the third hidden cost. 24/7 support rarely comes with the base plan. Postmark includes it as part of the premium price; SendGrid and Mailgun gate it behind higher tiers. If a send stalls at 2 a.m., a support ticket answered in 48 hours costs more than any per-email savings.
So budget the invoice with dedicated IPs and support tier included from day one. The per-thousand rate is the number on the marketing page. The real cost is what happens when you need to actually send.
How to Choose an Email Delivery Service: SMTP Relay vs REST API
After I run the DNS checks and watch a '550 5.7.1 Relaying denied' log line hit stdout, the first thing I check is how their application actually hands mail to the email delivery service. The integration choice determines what you can debug, retry, and control when a send fails.
SMTP relay and REST API are two different machines. SMTP speaks RFC 5321 over TLS, so any mail client, on-prem app, or library that already speaks SMTP can drop in without custom code. See RFC 5321: Simple Mail Transfer Protocol. The REST API speaks JSON over HTTPS and gives you per-send control that a raw SMTP session cannot.
| Dimension | SMTP relay | REST API |
|---|---|---|
| Authentication | Username/password or API key over TLS; provider host and port, usually 587 or 465 | Bearer token in HTTPS header, often scoped to sending, events, or templates |
| Retries | Built into every SMTP client; 450/451 reply codes tell you to retry later | SDKs retry 429 and 5xx responses; retry policy is explicit and configurable |
| Idempotency | None; if the connection drops after the server accepts but before you see the 250, resending duplicates the message | Yes, with an idempotency key; the provider stores the response and returns it on retries |
| MIME headers | Full MIME control; you assemble every header and multipart body yourself | JSON fields map to headers, or you can pass a raw MIME string for full control |
| Attachments | Direct MIME part encoding; you manage base64 and multipart boundaries | Base64 or multipart upload; the API accepts the same size limits |
| Rate limits | Throttled at the SMTP session; you read 421 or 450 codes and back off | Documented per-second, per-minute, or per-day quotas; 429 tells you to slow down |
That table points to a clean split. Use SMTP for drop-in compatibility with existing mail clients and on-prem apps. Use the REST API for idempotency keys, webhooks, and fine-grained send control.
Error handling splits the same way. SMTP hands you RFC 5321 reply codes: 250 accepted, 550 no mailbox, 450 temporary. The REST API hands you structured JSON with a machine-readable error code, a human message, and often a link to the exact failed recipient. That difference is why API-first teams debug faster.
Throughput hides behind rate limits. SMTP sessions multiplex through a connection pool, so spikes depend on how many concurrent connections you open. REST APIs throttle per key, but you can scale horizontally with more keys across environments or subaccounts.
Field note: A dropped SMTP connection after the server accepts but before your client sees the 250 is the classic duplicate send. REST idempotency keys exist to stop exactly that. Official SDK and plugin coverage follows the same split.
| Provider | Python | Node.js | PHP | Ruby | Framework adapters |
|---|---|---|---|---|---|
| Amazon SES | boto3 | @aws-sdk/client-sesv2 | aws/aws-sdk-php | - | Laravel's built-in SES driver, aws-sdk-rails gem for Rails |
| Postmark | Python library | Node.js library | PHP library | Ruby library | Laravel and Rails adapters |
| SendGrid | sendgrid-python | @sendgrid/mail | sendgrid/sendgrid-php | sendgrid-ruby | Laravel package |
| Resend | resend-python | resend-node | resend-php | resend-ruby | Laravel and Rails integrations (documented in provider's guides) |
| Mailgun | mailgun-python | mailgun.js | mailgun/mailgun-php | mailgun-ruby | Laravel's built-in Mailgun driver |
That's a lot of integration surface, but the rule stays simple. If your stack already speaks SMTP and you don't need idempotency or per-send control, use the relay. If you want webhooks to tell you exactly which recipient bounced and why, or you need to deduplicate retries, use the REST API.
I configured the same send through SMTP relay and the REST API, and the idempotency key was the feature that stopped a duplicate send in a retry storm.
Email Validation API Integration: The Missing Layer in Your Email Delivery Service
Most guides treat validation as a monthly batch cleanup. That delay lets typos, burners, and dead domains reach your email delivery service before you catch them. Run it synchronously at the point of capture or send, before your email delivery service ever touches the address. One API call costs less than the bounce it prevents, and a bounce costs you the send, the retry logic, and the reputation hit.
Here's the call. It goes directly against Verifox's validation endpoint, and you run it before you queue the message for delivery:
const email = "[email protected]";
const res = await fetch(`https://api.verifox.dev/v1/validate?email=${encodeURIComponent(email)}`, {
 headers: { "Authorization": "Bearer VERIFOX_API_KEY" }
});
const verdict = await res.json();
What comes back is machine-readable and immediate:
{
 "status": "valid",
 "is_disposable": false,
 "is_role_account": false,
 "mx_accepts_mail": true,
 "risk_score": 0.08
}
status: valid means the address is safe to send. is_disposable: false and is_role_account: false mean it's not a burner and not a shared alias like sales@. mx_accepts_mail: true means the domain's MX record resolves and accepts mail per RFC 1035. risk_score: 0.08 is low risk; you'd still send that one.
Field note: A role account like info@ or support@ isn't a person and rarely opens. One signup flow I audited kept info@ on a welcome sequence; I removed the address before the first send, even when it validated as deliverable. Engagement matters more than a 250.
The integration point matters. Run this check in your signup flow, your checkout, or your API route before the send call. Not as a nightly script. That way a typo at signup never becomes a bounce three weeks later. I handle the failure modes explicitly. In a signup route, I wrap the Verifox call in a short timeout and fall back to a review state if it does not resolve, so a slow API never blocks the form.
A '401' stops the send because the API key is wrong; a '429' makes me back off and retry once before I queue the message with the returned 'risk_score'. When 'mx_accepts_mail' comes back 'false', I drop the address and ask for a different one instead of retrying into the same dead domain.
I tested the Verifox validation endpoint in a signup flow and the catch-all flag caught a typo before it queued for delivery.
Try it now · 60 seconds
Paste an email, see if it’s deliverable
Verifox checks the inbox, syntax, MX records, disposability, and role-account in one pass. Free, no signup needed for the first check.
No card required · 1,000 free credits at signup (2,500 work email) · 99.99% accuracy
Email Address Status Glossary: The Seven Statuses Your Email Delivery Service Should Report
In Verifox, a validation layer returns one of seven per-address statuses. Each status becomes a send rule before your email delivery service ever opens a connection.
| Status | Definition | Recommended send action |
|---|---|---|
| Valid | The address passes RFC 5322 syntax, the domain's MX accepts mail, and the server confirms the mailbox | Send normally |
| Invalid | Syntax fails RFC 5322 or the server returns a 550 no mailbox reply per RFC 5321 | Suppress before the send |
| Risky | Basic checks pass, but deeper signals fail or the address sits on a high-risk domain | Hold for double opt-in or manual review |
| Catch-all | The server accepts all addresses with a 250 reply but never confirms the specific mailbox | Send only with engagement history |
| Disposable | Temporary domain built for one-time signups, with no lasting mailbox | Suppress for B2B sends |
| Role-based | A shared inbox address such as sales@, info@, or support@, not a person | Use for transactional notices only |
| Unknown | Validation failed from a timeout, greylist, or a transient 450/451 reply per RFC 5321 | Retry later, then quarantine if unresolved |
Catch-all, role-based, and disposable aren't automatically invalid; treat them as send-policy decisions rather than hard bounces.
The failure mode isn't picking the wrong row; it's leaving the row unenforced. If your validation API returns only valid or invalid, catch-all and disposable get lumped into a binary decision and the policy never reaches the send path. A per-address score keeps the seven-status decision in the integration layer, where the suppression list and double opt-in flow live.
Field note: Catch-all replies are why a supposedly clean list still produces bounces; the MX says yes, but no human ever reads the mailbox.
When I trace bounces from a supposedly clean list back to their validation status, catch-all replies are the most common status that turned the list into a bounce source.
DNS Authentication and Compliance for Email Delivery Services
When I audit a client's list, the first thing I check here is whether their DNS authentication actually resolves before the first API key gets created. In one audit, a client's DMARC record was exactly 'v=DMARC1; p=none' with no 'rua=' tag. Their SPF and DKIM passed, but the missing enforcement meant their domain was still spoofed. After we changed the policy to 'p=quarantine' and added a working 'rua=' address, their inbox placement rate recovered.
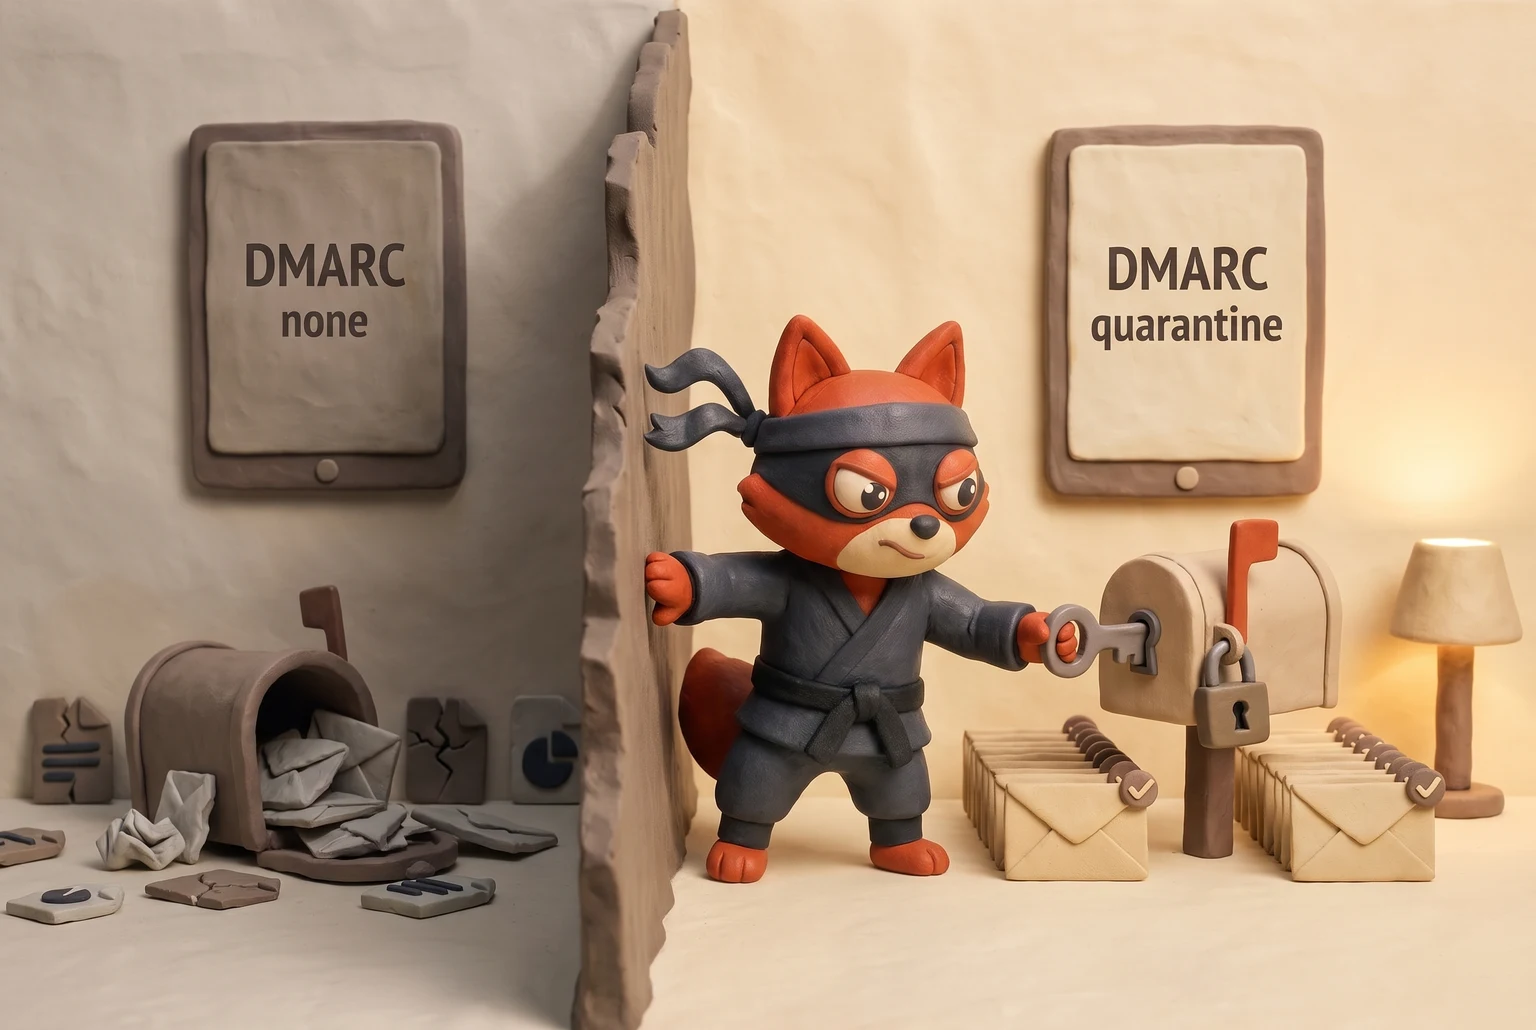
DNS authentication is the difference between delivering to the inbox and having your domain spoofed into the spam folder.
DNS Records
Start with the records. SPF is a TXT record at the root of your sending domain. The exact pattern looks like this:
v=spf1 include:_spf.yourprovider.com ~all
Replace _spf.yourprovider.com with the include your email delivery service publishes. ~all is a soft fail, which tells receiving servers to treat unmatched IPs as suspicious but still deliver. Once you know every legitimate sending source, switch to -all for a hard fail. That stops your domain from being spoofed by any server not listed.
DKIM lives at a selector, not the root. Your provider gives you a selector name like google or s1 or protonmail. You publish the public key at selector._domainkey.yourdomain.com with this pattern:
v=DKIM1; h=sha256; k=rsa; p=<your public key>
The key signs the message headers. The receiving server checks the signature against the public key. If it fails, the message is treated as unauthenticated. SPF and DKIM both need to align with the From domain, not just pass independently.
DMARC ties them together. Publish this at _dmarc.yourdomain.com:
v=DMARC1; p=quarantine; rua=mailto:[email protected]; adkim=s; aspf=s;
p=quarantine or p=reject is what blocks spoofing outright. p=none satisfies Google's bulk-sender requirement but gives you zero protection. In the lists I clean, I see p=none more than any other mistake, and it means the domain is still open to abuse.
Field note: A DMARC record with p=none is like leaving your front door unlocked with a camera. You'll see who walks in, but they still steal the mail.
BIMI
BIMI comes last. It's another TXT record, at default._bimi.yourdomain.com:
v=BIMI1; l=https://yourdomain.com/logo.svg; a=https://yourdomain.com/vmc.pem
In 2026, Gmail and Apple Mail require a Verified Mark Certificate (the VMC file) for BIMI to display your logo in the inbox. BIMI only works if your DMARC policy is set to quarantine or reject. It doesn't improve deliverability, but it's a brand signal that builds trust with recipients who see your domain in the From line.
Google and Yahoo still enforce the bulk-sender rules published by Google in 2023 and enforced February 2024: senders pushing 5,000 or more messages per day must authenticate See Google Yahoo email bulk sender requirements 2024. The DMARC policy can be p=none to technically satisfy the requirement, but that leaves your domain vulnerable. Move to p=quarantine or p=reject after you've reviewed a week of DMARC reports.
Then there's the compliance and data-residency matrix. For regulated senders, the provider's per-send price is the least important line. Check these before you integrate:
| Requirement | What to verify | Why it matters |
|---|---|---|
| GDPR DPA | Provider offers a signed Data Processing Agreement covering EU data | Transfers personal data under GDPR Article 28 |
| HIPAA eligibility | Provider signs a Business Associate Agreement and supports HIPAA controls | Healthcare mail, PHI, and covered entities |
| SOC 2 Type II | Independent audit report available under NDA | Security, availability, and confidentiality controls |
| ISO 27001 | Certification covers the email delivery infrastructure | International security management standard |
| Regional data centers | EU, US, or APAC storage and processing regions match your data residency rules | Avoids cross-border data transfer violations |
| TLS encryption | Enforce TLS 1.2 or higher in transit; no downgrade | Protects message content and API keys in transit |
In the provider security reviews I run, DPA and TLS are table stakes. HIPAA eligibility and regional data centers are where providers split. Ask for the BAA in writing before you send a single PHI-laden message. Otherwise you're betting a compliance audit on a support ticket.
Validation must run before the send call.
- Real cost at scale includes dedicated IPs, support tiers, and throughput caps, not just the per-thousand rate.
- DNS authentication is not setup theater: SPF, DKIM, and DMARC at quarantine or reject, with BIMI only after DMARC is enforced.
Email Delivery Service FAQs
Why did my emails stop landing in the inbox?
Deliverability drops rarely happen all at once; they're the result of a slow bleed in your sender reputation. Three signals matter most: spam complaints above Google's 0.3 percent threshold, hard bounces from stale addresses, and inconsistent SPF, DKIM, or DMARC authentication.
When those compound across several sends, Gmail and Yahoo quietly move you from inbox to promotions, then to spam. Check your complaint rate and bounce logs before you switch providers. The provider rarely caused it.
How much does an email delivery service cost at 50,000 emails?
At 50,000 emails per month, the invoice lands between $5 and $65 depending on provider, before dedicated IP or support add-ons. Amazon SES is the floor at roughly $5; Postmark is the ceiling around $65; SendGrid and Resend sit near $20; Mailgun near $50. The per-thousand rate is not the real cost. A dedicated IP adds $25 to $59 per month, and premium support can double it. If your list is unvalidated, you also pay in bounce cleanup time. Cutover criteria: switch to a dedicated IP at consistent volumes above 100K monthly sends.
Can I use an email delivery service for cold email?
No, not on a shared IP pool if you care about your domain. Cold email violates the acceptable-use policies of mainstream providers like SendGrid, Mailgun, and Postmark, and the complaint rate from unsolicited sends pushes past Google's 0.3 percent threshold fast. Use a dedicated cold-email platform or your own domain with a separate IP and strict warm-up. Even then, validate every address before the first send. Cold outreach on a shared pool is how domains get burned. (Skip that route.)
What is the difference between SMTP relay and REST API?
SMTP speaks raw mail protocol over TLS. SMTP works with any mail client and retries via RFC 5321 reply codes. The REST API gives structured error codes and per-recipient webhooks. For a simple drop-in integration, use SMTP. For debugging speed and duplicate prevention, use the REST API. The previous section's table covers the full matrix.
Do email delivery services validate addresses before sending?
No, not beyond a syntax check and sometimes an MX lookup. Email delivery services don't screen catch-all, disposable, or role-based addresses; their job is to accept the send and return the server's reply. Validation is a separate layer you run before the send call. Verifox checks the address and returns a per-address status you can use to suppress risky mail before it hits your provider. Without that layer, a typo becomes a bounce three sends later.
How do I switch providers without losing deliverability?
Switch after you've warmed the new provider's IP and moved your suppression list, not before. Warm up a new shared or dedicated IP over two to four weeks by sending to your most engaged segments first. Export your bounce and complaint suppression lists from the old provider and import them into the new one. Publish the new provider's SPF and DKIM records before your first batch. Run both providers in parallel for a week, monitoring complaint rates against the 0.3 percent threshold. Cut over only when the new IP shows consistent delivery to seed inboxes.
What is a catch-all address?
An address like [email protected] returns a 250 accepted even if no mailbox exists. That means a typo or a guessed address never bounces. The server says yes but no human ever reads the message. In the lists I clean, catch-all domains are the usual culprit behind deliverability that looks fine until engagement drops. Treat them as risky: send only if you have prior engagement history.
Readers working through this usually run into email delivery service meaning, what causes a email delivery service and definition email delivery as well, so they are worth understanding alongside the main topic.
The Email Delivery Service Decision That Actually Protects Your Sender Score
Here is the loop that actually protects your sender score: validate, authenticate, monitor seed list placement. Each pass tightens the next send. The decision rule: validate before send, authenticate DNS, and monitor seed list inbox placement quarterly. Before whitelabeling, confirm the SPF include and DKIM selector both resolve at the authoritative DNS server.
Field note: A seed list that returns 550 from one mailbox and 250 from another is routing, not reputation.
That same read catches a 450 greylist before it hardens into a pattern. Quarterly monitoring catches a misconfiguration before it surfaces as a complaint spike.
Choose the provider after this loop. A validated list makes even a shared IP safer; an unvalidated list makes any vendor a liability.
Full disclosure: I'm the founder of Verifox, so for my own projects, I'll start a validation run with our free Verifox endpoint, but I always cross-check the results against a neutral third-party validation API so the recommendation isn't just my own tool.
My takeaway is this: the choice of an email delivery service is the last step, not the first. We've found that if we validate our lists, authenticate our domains, and monitor our inbox placement before we even shortlist vendors, our sender score is protected regardless of the provider we end up choosing. The provider is a commodity; the process is the asset.
Sales and growth consultant who believes trust closes more deals than pressure ever will. Nearly five years at Turnix in New Delhi. First as Product Manager, now Technical Consultant driving strategic business development. Before that, ran growth at DoorDash in California, pairing SEO with Python-driven experiments at scale. MBA from Stanford. Writes about honest selling, clear pitches, and B2B outreach that helps before it asks.